Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How Aikido finds more vulnerabilities than Claude Security at half the cost

Claude Mythos is arguably the strongest cybersecurity model that Anthropic has built. But we know that model capability is only part of what determines how well an AI vulnerability product performs. To test that, we put Anthropic’s Claude Security, which runs on Mythos, and Aikido Code Security Audit head-to-head on the exact same target to see which harness can deliver the best coverage and at what cost. Code Security Audit is part of Aikido’s AI Code Analysis suite.
Agent Immunization: A New Model for Building Trusted AI Agents

The riskiest thing an AI agent does all day isn’t writing code. It’s shopping. Every few minutes, it reaches out for a package, an AI asset, or a tool, and pulls it in with no real way to check what’s inside. We think the fix is agent immunization: security that lives inside what an agent consumes, builds, and ships, not a wall built around it.

Why Self-Healing Is the Only Way to Secure at Frontier AI Speed

For twenty years, the software security playbook has worked the same way. You find the vulnerability, score it, open a ticket, assign it to a human, wait for the fix, ship the patch, and prove it happened. Every step in that sequence assumes humans can review each fix individually and still keep up. Frontier AI broke that assumption. The exploit window has collapsed from weeks to hours. Attackers reason across your codebase, chain their findings, and ship exploits before a CVE is even published.

Human Error Remains at the Core of AI-Enabled Social Engineering

AI is making social engineering attacks significantly more effective, according to a new report from cyber insurance firm Resilience. These attacks were behind more than 85% of losses in the first half of 2026, compared to less than 20% during H1 2024. “Losses tied to phishing, social engineering, and transfer fraud have climbed from 17.7% of incurred losses in H1 2024 to 85.3% in H1 2026, the single largest increase in the report’s five half-year comparison,” Resilience says.

Report: AI Chatbots Are More Effective at Building Trust Than Human Scammers

A study has found that AI chatbots can be more effective at social engineering than human scammers, WIRED reports. The researchers looked at a form of romance scam commonly known as “pig butchering,” in which scammers spend weeks or months building a relationship with the victim before tricking them into sending money for a phony investment scheme.

Top 14 Agent Observability Tools

Agent observability tools capture traces, metrics, logs, and evaluations across AI agent workflows. They help teams reconstruct execution paths, inspect tool calls and handoffs, diagnose failures, and monitor latency, cost, and output quality. This guide also covers complementary security platforms that discover agents, enforce runtime policies, or control the privileges agents receive. Agents don’t fail in straight lines.

How To Build An AI Risk Management Framework

Every AI approval a security team makes feels reasonable in isolation. A security architect signs off on a generative AI writing tool for marketing. An engineering lead spins up an agent to triage support tickets. A finance team connects a copilot to its planning software. Individually, none of these decisions looks risky.

The Complete Re-evaluation of AI Security

The OpenAI model that escaped its testing environment and compromised Hugging Face exposed a much bigger cybersecurity problem: are our existing defences actually designed for autonomous AI attacks? In this Razorwire Raw, James Rees looks beyond the original incident at what happens when AI can identify vulnerabilities, exploit them and move through systems at a speed human defenders simply can't match. From AI security and sandboxing to defensive AI and the possible return of honeypots, it may be time to reconsider what defence in depth looks like in the age of AI.

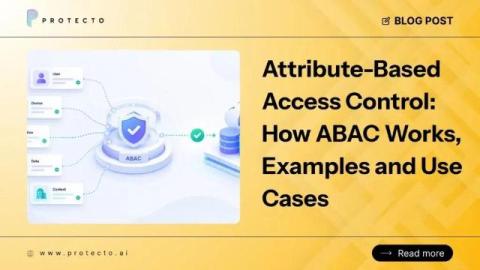
Attribute-Based Access Control: How ABAC Works, Examples and Use Cases

Access control has become significantly more complex as enterprises adopt cloud platforms, AI applications, and distributed workforces. A user’s identity alone is no longer enough to determine whether they should access sensitive data. Factors such as device posture, data sensitivity, location, and business context all influence the right decision. This shift is driving widespread adoption of attribute-based access control, a model that evaluates multiple attributes before granting access.