Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Secure AI Written Code Before It Ships: Salt Code

AI coding assistants are transforming how enterprise software gets built. Developers at every level are prompting their way to production-ready APIs, MCP integrations, and agentic workflows faster than any security team can review them. The problem is that none of those assistants knows your internal security standards, regulatory obligations, or risk tolerance. The result is insecure patterns shipping unnoticed, vulnerabilities discovered downstream when fixes are costly, and compliance becoming a guessing game on every commit.
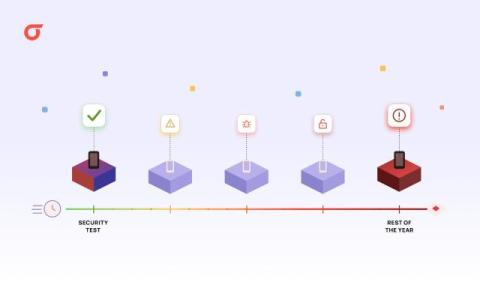
Why Annual Mobile App Security Testing Is Not Enough on Its Own

Annual testing secures a moment. Your app keeps changing. Here is how to cover the interval between assessments. An annual penetration test answers a precise question. Was this version of this application secure when a skilled tester examined it? That answer has real value. It is independent, deep, and finds business logic flaws that no scanner will ever surface. It is also a photograph.

How NER Finds Sensitive Data Hidden in Documents #shorts

Sensitive data detection was much easier when information lived inside structured databases. Tables, columns, field names, and predictable data types gave security teams a clear map of where sensitive information lived. But when sensitive data moved into documents and PDFs, that map disappeared. Names, addresses, phone numbers, credit card numbers, and other sensitive information could be buried inside natural language.

We Had 13 Engineers Spend Three Months Finding Vulnerabilities with LLMs

Blame for all flaws belongs to the flawed human author. Historically, the bottleneck for finding security bugs in software was human bandwidth. As pointed out in this great post by Tom Ptacek, it appears that large language models are exceptionally good at finding them with simple prompting. This adds substantial bandwidth to the effort of finding bugs.

AI adoption and third-party risk implications: How to close the governance gap

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Remediation Agents, Demystified: Why Fixing Beats Finding

Six new security issues for every one issue remediated. That's the ratio Snyk research has found, and it's why the AI Security Engineers Community gave an hour of livestream time to fixing rather than finding. Play Video: Remediation Agents Demystified: Your AI Teammate for Fixing Security Bugs Remediation Agents Demystified paired a fireside chat with a live demo.