Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How to Use AI to Turn Images into Engaging Video Content

Video has become one of the most effective ways to communicate online. From social media posts to product promotions, businesses and creators increasingly rely on video to capture attention and reach wider audiences. However, producing video content can take significant time and resources. Writing scripts, recording footage, editing clips, and adding effects can quickly turn a simple idea into a lengthy production process.
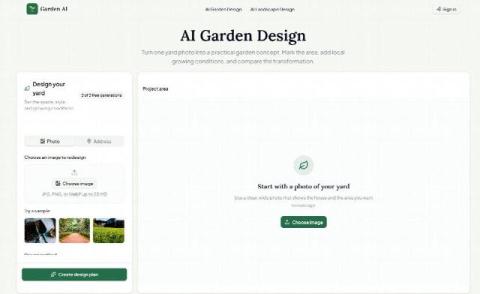
How a Solo Garden Designer Cut Concept Time in Half with AI Tools

I used to spend entire evenings sketching rough layouts for clients who just wanted "something prettier than the current yard." By the time I produced three decent options, the client had already moved on or decided the project could wait. That cycle was exhausting and expensive for both of us.

The Financial Imperative of Garage Door Security in Long Island

To effectively break-in proof a smart garage door in Long Island, homeowners must combine structural reinforcements with advanced digital encryption. The definitive strategy requires upgrading to a solid insulated steel or wood door, integrating a smart opener equipped with military-grade rolling code technology, applying opaque films to visible windows, deploying motion-activated surveillance cameras, and physically securing the emergency release mechanism. These comprehensive measures successfully neutralize both brute-force physical entry tactics and sophisticated radio-frequency signal hacking.

How Mobile App Agencies Use GPS and Fintech Expertise to Build Smarter Apps

What happens when an app knows not just who a user is, but where they are and how they'd prefer to pay? Location and financial technology stop behaving like separate features and start functioning as one connected layer of the experience. In a market like Melbourne, where mobile products increasingly need to work across commuting, retail, delivery, and everyday payments, that combination is often the difference between an app that feels genuinely useful and one that just checks boxes.

Why Is a Reranker Needed in RAG If We Have a Retriever?

Enterprise RAG pipelines have a recall stage and a precision stage. The retriever handles recall. The reranker handles precision. Skipping the reranker, or misplacing security controls around it, is where most accuracy and data exposure problems begin. The retriever’s job is to pull back every document that might be relevant. The reranker’s job is to find, from that candidate set, the documents that actually answer the question.

From AI Findings to Action: How Security Teams Should Triage AI-Discovered Vulnerabilities

Security teams didn’t need a headline to tell them that vulnerability volumes continue to be problematic. The CVE database now contains over 354,000 records. Annual disclosure rates have climbed steadily for more than a decade. And remediation backlogs have long been recognized not as an aberration, but as a fixture of the job.

AI Supply Chain Security: Why an SBOM Cannot Cover It

A software bill of materials works because software changes through a build. Someone bumps a dependency, the pipeline runs, the manifest updates and a scanner compares the new list against known vulnerabilities. Every part of that loop assumes a rebuild is the thing that changes behavior. ‍ AI systems break that assumption at the point it matters most. Editing a system prompt changes what a model does, swaps no dependency, triggers no build and produces no new manifest.

What OpenTelemetry Can Actually Tell You About Your AI Agents

‍ The distance between what OpenTelemetry was built for and what AI governance is asking of it shows up in a single number. Distributed tracing descends from Dapper, the 2010 Google paper that gave the industry the vocabulary of traces and spans. Dapper sampled one trace in 1,024. That is ample for finding a latency regression, because a regression recurs and the next sample catches it.

The Hidden Cost of BOLA/BFLA Vulnerabilities: A CISO's Guide to Quantifying Risk

Every CISO managing an API estate has heard of Broken Object Level Authorization (BOLA) and Broken Function Level Authorization (BFLA). What is harder to pin down is what these vulnerabilities actually cost the business when they go unaddressed. Board members and finance teams want numbers, not acronyms, and that gap between technical risk and financial risk is where security budgets get lost. BOLA has held the number one spot in the OWASP API Security Top 10 since the list was created in 2019.