Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Request, Aggregate, Bypass: How Attackers Can Evade LLM Safety Classifiers

Modern frontier AI models deploy safety classifiers. These are second AI models that sit between the user and the frontier model, evaluating every request in real time. If a request is flagged as harmful, the classifier blocks it before the model can respond. Significant investment and safety model expertise have made these classifiers effective. Anticipating how adversaries circumvent these systems is a security problem that requires different expertise.

AI Governance Where the Regulator Also Runs the Market

AI governance evidence is usually prepared for a neutral reader. A regulator with no stake in the market, an auditor with no competing product, an examiner who gains nothing from what the documentation contains. ‍ In securities and derivatives markets that assumption does not hold. Exchanges and clearing organizations register as self-regulatory organizations, and most of them operate the market while regulating its participants. The reader of your evidence is also an operator. ‍

See Falcon for XIoT in Action.

CrowdStrike's Falcon for XIoT addresses challenges in managing complex industrial and clinical environments by providing visibility into operational assets. The solution helps teams prioritize vulnerabilities based on operational impact rather than severity alone, ensuring safe decisions while minimizing interruptions. Through a detailed investigation process, users can assess asset profiles, validate exposures, and implement controlled responses tailored to specific risks. This approach optimizes asset management and enhances safety in both operational technology (OT) and clinical settings.

Securing Your AI Agents: Native AI Detection and Response Across the Full Agentic Path

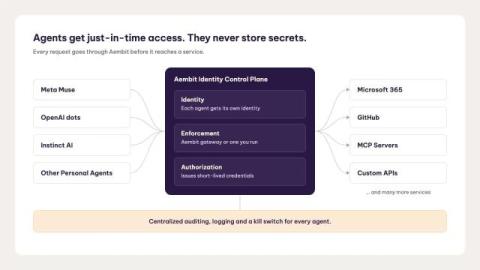
Enterprises are deploying AI agents at scale, and those agents are taking real business actions. Through LLMs, MCP servers, and APIs, they move money, access patient records, modify code, and send emails. The attack surface has fundamentally shifted, but most security programs are still focused on what an AI says rather than what it does.

Governing at the speed of AI: What IT leaders need to know

AI is reshaping the IT leadership role faster than any shift in the last decade. As AI makes it dramatically easier to build software (agents, apps, automations, and more), the volume of software entering the enterprise is far beyond what IT teams have had to govern before. That shift demands new ways of thinking about enterprise control: how security, access, and oversight evolve to keep pace with software that's built faster and by far more people than ever before. The leaders who treat this as an operating shift, not just a technical one, are the ones expanding their influence.

Build the Self-Driving SOC with Tanium Security Operations

Attackers don't wait for humans, and neither should your SOC. Tanium Security Operations brings detection, investigation, hunting, and response together on one platform that moves at machine speed. See how Tanium Atlas works as an extension of your team: pulling live telemetry, historical activity, and the full process tree the moment a threat surfaces, hunting a hypothesis across every endpoint in your fleet, and containing threats from one endpoint to hundreds of thousands. When the hunt needs to go deeper, HuntIQ's hands-on experts take it from there, inside your environment.