Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

New Prompt Injection Techniques Cover Agent-Planning Attacks

Prompt injection started as a simple idea during its initial chatbot phase: Tell the model to ignore its instructions and return information in violation of its guardrails. Now, prompt injection attacks can aim at something harder to see: how an agent plans, and how a model reasons and decides which rules apply.
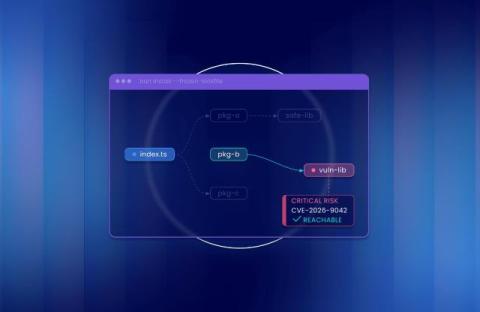
Mend SCA now supports Bun, with reachability built in

TL;DR: Mend SCA now scans Bun-managed JavaScript and TypeScript projects, including both the text-based bun.lock and legacy binary bun.lockb lockfiles. It detects direct and transitive dependencies automatically, works in the Mend CLI and every repository integration, and supports reachability analysis so teams can fix the vulnerabilities their code actually calls first.

Securing the Future of AI

How Kroll and CrowdStrike Are Turning Innovation into Value for Customers At Fal.Con 2026 in Las Vegas, Kroll Managing Director Robb Mayeski joined CrowdStrike Vice President of Global Scale Partnerships Dan Danielli for a live interview with theCUBE, SiliconANGLE. The discussion explores how Kroll and CrowdStrike are helping organizations defend against AI-accelerated threats while adopting AI in a way that delivers measurable business value and strengthens cyber resilience.

Forward Threat Exposure: Know What an Attacker Can Reach

Cybersecurity is reaching an inflection point. Attackers use AI to research vulnerabilities, develop exploits, and run increasingly automated campaigns, compressing the time defenders have to respond. As that window shrinks, defenders need to know which vulnerabilities an attacker can actually reach. Answering that question is difficult when security tools provide separate views of vulnerabilities, assets, and network controls.

Business IT Support: Should You Outsource or Keep It In-House?

For most small businesses, outsourcing business IT support gives more cover for less money than hiring your own IT person. Some firms prefer to keep IT in-house for direct control, and many larger ones combine their own team with a provider, an approach called co-managed IT. The choice affects more than your IT bill. It decides who spots problems and fixes them, and whether your IT knowledge stays with the business when someone leaves.

AI-accelerated Vulnerability Discovery Demands Rethinking Vulnerability Management Practices

Enterprise security has a speed problem. Attackers are getting faster at finding and exploiting vulnerabilities, while many organizations still rely on ticket-based remediation, approvals, and scheduled maintenance windows. AI threatens to widen that gap considerably, exposing one of vulnerability management’s largest unchanged challenges: getting the right systems to fix the right problems before attackers exploit them.

Cloudflare DDoS Threat Report 2026 Q3: More swarms, fewer giants

Welcome to the 26th edition of Cloudflare's DDoS Threat Report. This edition covers the third quarter of 2026 — July, August, and September — and returns the series to its quarterly cadence following the combined H1 2026 volume. The analysis is produced by Cloudforce One, Cloudflare's Threat Intelligence organization, providing a comprehensive analysis of the evolving threat landscape of Distributed Denial of Service (DDoS) attacks based on data from the Cloudflare network.

Threat Actors to Watch 2026: APT41 and UAC-0099

CYJAX profiles APT41’s BlackX UEFI bootkit campaign against Central Asian diplomatic agencies and the UAC-0099 and Sandworm compromise of a Ukrainian grain logistics company, with key takeaways and defensive guidance. APT41 is using a UEFI bootkit against Central Asian diplomatic agencies, while UAC-0099 appears to have handed a backdoor to Sandworm in Ukraine. CYJAX breaks down both threats and what defenders should do next.

AI used in Aur0ra ransomware testing and execution

In May 2026, Counter Threat Unit (CTU) researchers published a report on an AI-assisted post-exploitation framework that tested the capabilities of multiple vendors’ endpoint detection and response (EDR) solutions, including the Sophos agent. Following a testing phase, Sophos analysts observed the same infrastructure hosting Cobalt Strike in support of Aur0ra ransomware (also known as Aurora ransomware) operations.