Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

A Simpler Way We Release and Support Every Product

A plain-language look at our new release and support policy — and what it means for you, no matter which product you run. For customers and partners, release and support practices have not always been easy to interpret. Different products used different terms for similar things — major and minor releases, patch releases, hotfixes — which made it hard to know which release to adopt, how long it would be supported, or whether a given update added functionality or only fixed something.
Introducing LimaCharlie Email Security: One Phish, Start to Finish

Introducing LimaCharlie Email Security. It connects to Microsoft 365 or Google Workspace through the provider's API, with no MX change and nothing in the delivery path, and shows the signals behind its verdicts. This walkthrough follows one malicious email from its 94/100 verdict through how the score compounds, a benign contrast with its measured processing timeline, the evidence, link analysis, response at the provider, hunting across the organization, groups and campaigns, user reports, the rule that caught it, policy, and email as telemetry for detection and response rules.

How Understanding TMS Cost Arizona Enhances Treatment Affordability

Transcranial Magnetic Stimulation (TMS) therapy is a groundbreaking treatment option for individuals with mental health conditions such as depression. As more people in Arizona seek effective alternatives to medication, understanding the financial aspects of TMS therapy becomes essential. This article delves into how TMS therapy is revolutionizing mental health treatment, factors influencing its cost, insurance coverage possibilities, and strategies for improving treatment affordability. By the end, you will have a comprehensive understanding of how these elements impact the overall expense of TMS therapy.

Need a Better Android App? Here's How to Find One You Can Trust

The best way to find a trustworthy Android app is to check its developer, permissions, reviews, Data Safety information, and update history before installing it. I have installed plenty of Android apps over the years, and I have learned that a high rating or millions of downloads do not always tell you enough. Some apps look useful at first but end up showing excessive ads, demanding unnecessary permissions, or frequent crashing after a recent update.

Prop Firm Alternatives Compared: What Fast, Secure Payouts Actually Look Like

For prop traders, a payout is the moment the whole process becomes real. It's also where trust gets tested, because a slow or unexplained delay can undo months of disciplined trading. That makes payout handling a security question as much as a customer service one. How a firm verifies requests, protects the funds behind them and moves money out says a lot about how seriously it takes risk. This guide looks at what a well-run payout process involves, then compares five prop firms traders often weigh against each other.

XWorm Malware: Worming Its Way From Entry to Exploitation

XWorm is a versatile modular malware that presents a multifaceted threat landscape. This malware can be employed for various malicious purposes, including remote access, data theft, ransomware delivery, and botnet creation. Despite being relatively new in the cyber threat landscape, XWorm has rapidly gained notoriety, largely due to its association with the DDGroup cybercrime group, renowned for its utilization of advanced malware techniques.

Supply Chain Attacks in the SaaS Era: Unpacking the Drift Breach | Cloudflare x The CISO Signal

It was just a little chat window in the corner of the screen. But behind it was a web of trusted connections reaching deep inside the enterprise. Here’s how attackers turned a trusted integration into a massive supply chain breach. Expand for more details and resources In August 2025, attackers tracked as UNC6395 compromised OAuth tokens associated with Salesloft’s Drift integration. This turned trusted connections to Salesforce environments into an attack path reaching hundreds of companies, including top-tier cybersecurity organizations.

Emerging Threat: (CVE-2026-84411) MikroTik RouterOS Unauthenticated Root RCE via Web Management

CVE-2026-84411 is an integer underflow in the web management service of MikroTik RouterOS, classified as CWE-191. The flaw sits in the service’s HTTP request body handling and is reachable before authentication. A single crafted request lets an unauthenticated network attacker execute arbitrary code as root, or crash the device. The vulnerability carries a CVSS v3.1 base score of 9.8 (Critical) and a CVSS v4.0 base score of 9.3 (Critical).

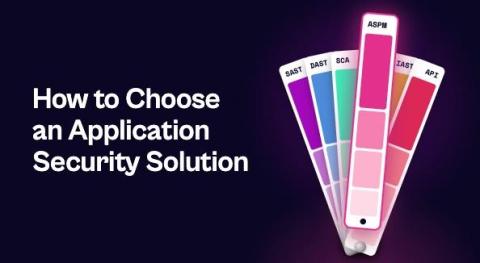
How to Choose an Application Security Solution

Most teams need a combination of application security tools rather than a single one. Common categories are SAST, DAST, IAST/RASP, SCA, API and container security, and ASPM, and each covers a different stage of development. When you evaluate options, look for coverage that matches your stack, integration with developer workflows, accurate findings, risk-based prioritization, and actionable remediation guidance.