

|
By Adi Bleih
Grandoreiro is a malware family classified as a backdoor and spyware, first seen in April 2020, and is consistently described as a banking trojan focused on credential theft, remote fraud enablement, and control of compromised Windows systems. It has remained active through recurring campaigns, including a renewed wave in May and June 2026 that concentrated heavily on Latin America, especially Mexico, while also reaching parts of Europe and North America.

|
By Adi Bleih
RevStealer is an infostealer first observed in September 2026 that targets Windows systems, with reported 64-bit execution and JavaScript-based components. It is built to steal authentication credentials and other sensitive user data while emphasizing stealth through anti-debugging, anti-sandbox, anti-VM, and evasion features. Its threat significance comes from a short, theft-focused execution model that pairs broad data collection with concealed command-and-control and exfiltration behavior.

|
By Adi Bleih
RecordBreaker is a malware family first observed in July 2022 and classified as both an infostealer and banking trojan. It targets x86 and x86-64 environments and is built to steal authentication data, collect system and user information, communicate with command-and-control infrastructure, and install additional components. Its operational profile also includes remote machine access, fraud-enabling activity, and system control, making it a flexible post-compromise tool.
|
By Adi Bleih
XWorm is a versatile modular malware that presents a multifaceted threat landscape. This malware can be employed for various malicious purposes, including remote access, data theft, ransomware delivery, and botnet creation. Despite being relatively new in the cyber threat landscape, XWorm has rapidly gained notoriety, largely due to its association with the DDGroup cybercrime group, renowned for its utilization of advanced malware techniques.
|
By Adi Bleih
SalatStealer is a Go-based infostealer family first observed in August 2026, built for x86 Windows environments and focused on credential theft. Its documented capabilities include stealing authentication credentials, hiding executing code, and degrading security software.
|
By Adi Bleih
MovieReaper is a malware family first observed in September 2026 that combines remote-access trojan and loader functionality in a modular, multi-stage framework. It targets x86-64 systems and is built to reach remote machines, install additional components, persist across reboots, and exfiltrate data while resisting analysis through anti-sandbox, anti-VM, and AV-evasion features.
|
By Adi Bleih
Noodle RAT—also known as ANGRYREBEL or Nood RAT—is a modular remote access trojan (RAT) with dual versions for Windows and Linux, actively used by Chinese-speaking threat actors since at least mid-2016. It was previously misclassified as variants of Gh0st RAT or Rekoobe but is now recognized as a unique backdoor family.
|
By Adi Bleih
DarkTortilla is a sophisticated and adaptable.NET-based crypter, active since at least August 2015, known for delivering a range of malicious software, including prevalent information stealers and remote access trojans like AgentTesla, AsyncRat, NanoCore, and RedLine.
|
By sophiakl
Originating in early 2023, Pikabot emerged as a significant malware loader. Over the past year, ThreatLabz has diligently monitored its development and operational methods. Notably, there was a surge in Pikabot’s usage in the latter part of 2023, attributed to a BlackBasta ransomware affiliate adopting Pikabot post the FBI-led Qakbot takedown. However, Pikabot’s activity ceased shortly after Christmas 2023, with version 1.1.19 marking its endpoint.
|
By Adi Bleih
PoshC2 version 6.0, an open-source command and control framework, is notable for its robust capabilities in managing compromised hosts. Accompanying its release, a comprehensive list of Indicators of Compromise (IoCs) and a dedicated GitHub repository have been provided. These resources are designed to assist cybersecurity teams in detecting PoshC2, especially when deployed with its default settings, which less sophisticated attackers often utilize.
Check Point Exposure Management Safe Remediation Demo: Harden Firewalls, Endpoints Operating Systems
Closing an exposure should not cause an outage. See how Safe Remediation in Check Point Exposure Management turns findings into validated fixes on the security controls you already own, without business disruption.
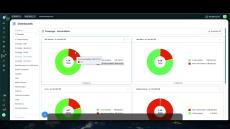
No single security tool shows the full picture. See how Check Point Exposure Management pulls findings from dozens of tools into one view, so your team can see which assets are exposed, which controls are missing, and what to fix first.
See how Check Point Exposure Management connects external threat intelligence with what is exposed inside your environment, so your security team knows which threats matter and what to fix first. In this 14-minute walkthrough, Check Point Software shows how Check Point Exposure Management turns 15 years of threat intelligence collection, covering the deep and dark web and threat capture monitoring, into prioritized, actionable exposure data. You see which threat actors and campaigns are relevant to your organization, which vulnerable hosts they could reach, and how to block them in real time.
Complete CTEM Use Case: From Exposure Alert to Safe Remediation with Check Point Exposure Management
One vulnerability, five steps, start to finish. Watch how Check Point Exposure Management finds an exposed asset, proves it’s exploitable, shows who is exploiting it, locates every affected host, and closes the gap through your existing security controls.
Threat intelligence only helps when your team can act on it. See how Check Point Exposure Management collects intelligence from the clear, deep, and dark web, adds telemetry from Check Point’s global firewall network, and ties it to what is exposed in your own environment.
Check Point Agentic Exposure Validation (AEV) uses AI agents to reason like an attacker across your external footprint. It correlates your assets with live threat intelligence, exploit research, and attacker behavior, and tells you, in minutes, what's actually exploitable and what isn't. No assumptions. No noise. Evidence-backed findings your team can act on immediately.
Exposure Management isn’t just a buzzword; it’s the future of cybersecurity. Attackers move fast, exploiting misconfigurations, leaked credentials, and control gaps before patch cycles even start. Traditional tools give you dashboards and alerts, but visibility without action is just noise.
The question isn’t if something goes wrong, it’s whether you can fix it fast enough….. This is why we built Check Point Exposure Management.
|
By Cyberint
Safe Remediation is the process of turning validated exposure insights into coordinated, non-disruptive fixes across security controls ensuring teams can reduce risk quickly without breaking production. More specifically, Safe Remediation includes: Validation before enforcement Remediation without downtime Automated, coordinated action across controls Preemptive blocking of attacker infrastructure Safe-by-design automation Safe Remediation ensures that exposures are fixed quickly, automatically, and without operational risk – turning detection into trusted, validated action.
|
By Cyberint
See how customers can query our MCP server to sift through their threat intelligence and get contextual answers immediately.
- October 2026 (9)
- September 2026 (4)
- August 2026 (4)
- July 2026 (4)
- June 2026 (3)
- May 2026 (1)
- April 2026 (1)
- January 2026 (2)
- December 2025 (7)
- November 2025 (2)
- September 2025 (4)
- July 2025 (6)
- June 2025 (2)
- May 2025 (6)
- April 2025 (4)
- March 2025 (2)
- February 2025 (5)
- January 2025 (4)
- December 2024 (8)
- November 2024 (6)
- October 2024 (5)
- September 2024 (6)
- August 2024 (5)
- July 2024 (5)
- June 2024 (6)
- May 2024 (9)
- April 2024 (7)
- March 2024 (3)
- February 2024 (8)
- January 2024 (9)
- December 2023 (6)
- November 2023 (9)
- October 2023 (14)
- September 2023 (11)
- August 2023 (9)
- July 2023 (9)
- June 2023 (8)
- May 2023 (7)
- April 2023 (9)
- March 2023 (8)
- February 2023 (5)
- December 2022 (3)
- November 2022 (4)
- October 2022 (5)
- September 2022 (6)
- August 2022 (5)
- July 2022 (4)
- June 2022 (3)
- May 2022 (4)
- April 2022 (4)
- March 2022 (8)
- February 2022 (6)
- January 2022 (2)
- December 2021 (7)
- November 2021 (4)
- October 2021 (2)
- September 2021 (3)
- August 2021 (4)
- July 2021 (7)
- June 2021 (3)
- May 2021 (6)
- April 2021 (5)
- March 2021 (4)
- February 2021 (5)
- January 2021 (12)
- December 2020 (6)
- November 2020 (2)
- October 2020 (4)
- July 2020 (1)
- May 2020 (1)
- April 2020 (2)
- March 2020 (3)
- January 2020 (1)
- December 2019 (2)
- September 2019 (1)
- May 2019 (1)
- March 2019 (1)
- November 2018 (1)
- January 2018 (3)
- May 2014 (2)
Best-in-class managed intelligence suite. We help you identify emerging threats, verify your security posture, and respond effectively to reduce their impact.
CyberInt's Managed Detection and Response services span globally and include some of the top finance, retail and telecommunication organizations. Allowing our customers to combat and respond to advanced cyber threats that would normally go unnoticed by standard security controls, while protecting their brand, digital assets and customers.
Solutions:
- Threat Intelligence: Real-time monitoring of threats in the deep, dark and open web such as phishing and malware campaigns, brute-force and credential stuffing threats, data leakage, including personal identifiable information (PII), and fraudulent activity.
- Digital Risk: Digital footprint discovery and ongoing monitoring of organizations’ cloud and external facing assets. Ensuring visibility into assets with severity-based prioritization of issues to address, highlighting related threats, vulnerabilities, and weaknesses.
- Threat Hunting: Driven by Cyberint proprietary intelligence and custom detections service provides continuous hunt for threats across the IT and infrastructure. Leveraging 3rd party EDR-agnostic technology and SOAR, we deploy proprietary automated playbooks to contain and mitigate threats within minutes.
- Cybersecurity Assessment: Testing applications and infrastructure’s resilience to cyberattacks, to identify weaknesses and loopholes in your security posture.
Intelligence-driven Detection & Response. Leveraging threat intelligence suite, threat hunting and threat mitigation and response services.