Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

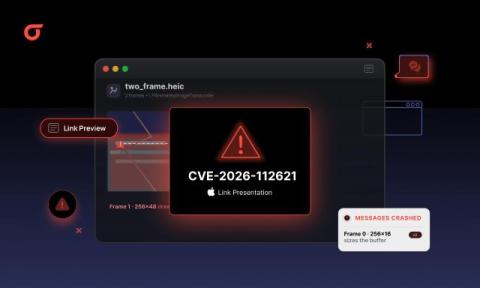
CVE-2026-112621: How a Link Preview Could Crash Apple Messages

In this blog, I'll explain how I found the LinkPresentation out-of-bounds write, later assigned CVE-2026-112621 and fixed in iOS 27.2 and macOS Golden Gate 27.2. LinkPresentation is the framework Apple uses to build link previews, and on an unpatched Mac, one crafted preview in Messages was enough to crash it. That fix shipped on October 26, 2026, and Apple credited me, Vinay Kumar Rasala (Xplo8E) of Appknox, alongside an anonymous researcher.
AI agent security in Kubernetes: Why prompt injection isn't the right term

This post is based on Mackenzie's conversation with Abdel Sghiouar on The Secure Disclosure podcast. Listen to the full episode or watch below. If you give an agent the run of your cluster, it can trace a problem through every layer of the stack faster than any on-call engineer. But that same reach makes the agent worth hijacking.

Cybersecurity Awareness Month: Securing the Next 250 with Cyber Threat Hunting

October has made a strong case for this year’s Cybersecurity Awareness Month (opens in a new tab) theme, “Securing the Next 250,” chosen in honor of the U.S.’s 250th anniversary. The initiative, started by the Cybersecurity and Infrastructure Security Agency (CISA) and the National Cybersecurity Alliance (NCA), occurs annually in October to raise awareness about online safety and empower individuals and businesses to protect themselves from cybercrime.

eMudhra CA Key Exposure: How miniOrange PAM Enables Control

The eMudhra CA key exposure involved eight intermediate certificates generated with weak private keys. Although the affected intermediates had not issued publicly trusted end-entity certificates, changes to certificate trust stores created a need to identify dependencies and plan certificate replacement across affected environments.

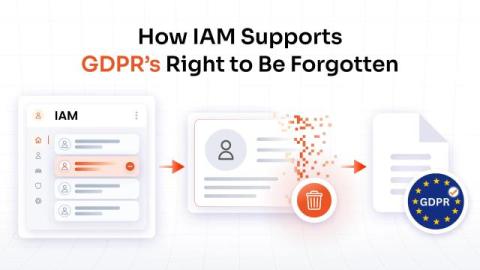
How IAM Supports GDPR's Right to Be Forgotten

Deleting a user account takes seconds. Deleting everything your organization knows about that user is a much bigger job. When a customer invokes their right to be forgotten, their profile in your identity provider is only the starting point, because their details also live in your CRM, support desk, billing tool, analytics platform, and a few SaaS apps your marketing team connected last year. Every one of those copies has to be found and dealt with before the legal deadline.

The First Questions That Matter: Triaging AI Agent Security Incidents

I have lived through major incidents firsthand, including the urgent calls that come in the middle of the night. In my experience, the teams that contain damage quickly are not the ones with the most tools. They’re the ones that ask the right questions in the first hour.

Cato CTRL Threat Research: PHP2Shell Exploitation Attempts in the Wild, and How Cato IPS Blocked Them

On 21 October 2026, PHP released fixes for CVE-2026-109618 and CVE-2026-109619, a pair of critical runtime vulnerabilities known as PHP2Shell. One day later, we described how our self-evolving CVE mitigation agent turned the patch into reviewed IPS protection in minutes. This report follows what happened next, including how quickly attackers moved, what their attempts looked like, and how Cato’s cloud-delivered IPS protection blocked them on inspected customer traffic.

Malicious Claude Code extension distributed through Cursor marketplace

On October 29, 2026, Cursor reported that a malicious version of Anthropic’s Claude Code extension (2.1.313) was available in the Cursor extension marketplace between approximately 09:27 and 20:35 UTC. Cursor identified impacted macOS and Windows packages and estimates that up to 5,000 users were affected.

The Dishwasher Doesn't Need a Soul, The Film Does.

People say they can spot AI writing a mile off. The em dashes. The word “delve.” The LinkedIn posts that begin with “I’ve been thinking a lot about leadership” and end without a single thought. I understand the reaction. I’ve read enough of them to develop a thousand-yard stare every time someone says they’re “unlocking” something. But I also don’t believe that all AI uses need to be thrown into the waste bin.