Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

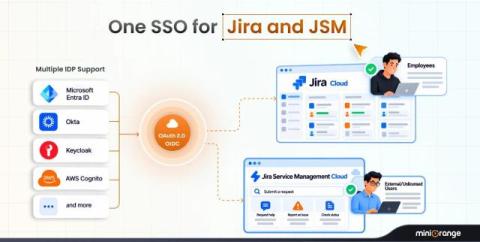
Why OAuth SSO Matters for Both Jira Cloud and Jira Service Management

Jira is rarely used by just one type of user. Primarily, teams use Jira Cloud for project management. At the same time, support teams work inside Jira Service Management (JSM), while internal employees and external users such as customers, vendors, and partners may access the JSM portal. They are all accessing the same Atlassian ecosystem, but they do not necessarily log in the same way. This is where organizations can run into a problem.
One Identity: Governing Every Identity - Human, Machine, and AI

Every enterprise runs on identity — and machines and AI agents now outnumber people in many environments. This 2-minute overview covers why identity has become a board-level priority, and how One Identity governs every identity — human, machine, and AI agent — on one unified platform. Validated by Omdia: 150% ROI, go-live in as little as one day, zero-touch onboarding.

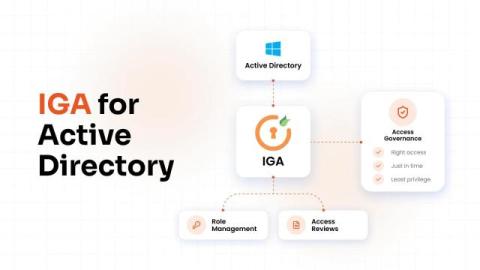
Active Directory Governance: How to Know Who Has Access and Why

An employee changes roles. Their manager requests access for the new job, and IT grants it quickly. That part works well. The issue appears when access from the previous role stays in place. The same thing happens when a contractor finishes a project, an admin completes urgent work, or a team retires an application. Access often remains because nobody has checked whether it still serves a purpose. Active Directory governance allows IT and security teams to answer three questions.

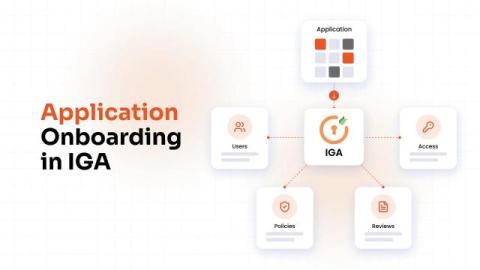
Application Onboarding in IGA: A Practical Guide

Application onboarding is the process of integrating an application with your identity governance and administration platform so its accounts, roles, and entitlements can be governed. Once an application is onboarded, you can: Without onboarding, an application stays outside your controls, and any access inside it is invisible to your security and audit teams.

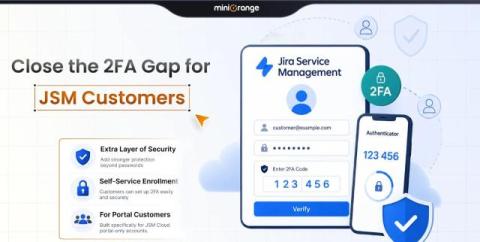
2FA for JSM Cloud Portal Customers: Closing the Gap Atlassian Guard Leaves Open

Atlassian Guard protects your employees through SSO and MFA. It does not cover portal-only customer accounts. However, customers need to access your Jira Service Management (JSM) portal to raise tickets and do so securely. But they often use portal-only accounts, which, in most cases, are protected only by a password. You’ll have security gaps if they don’t authenticate the same way as your employees. You must understand what the limits of Atlassian Guard are.

Difference between Network DLP vs Endpoint DLP vs Cloud DLP

When it comes to protecting business-sensitive data, understanding the difference and the scope of Network DLP, Endpoint DLP, and Cloud DLP is essential. Each of these Data Loss Prevention solutions (DLP) plays a unique role in securing data across various environments, whether it is on the Network, on individual devices, or in the Cloud. Knowing how each solution works can help you determine the best approach to safeguard your organization's sensitive information.

What Is Kiosk Mode and How Does It Work?

Customer engagement plays a major role in how businesses retain users and build lasting relationships. Whether it’s a retail store, a logistics operation, or a healthcare facility, the way people interact with devices directly impacts efficiency and experience. This is where kiosks come in. Modern businesses increasingly rely on POS and kiosk-driven interactions to simplify workflows and improve customer satisfaction.

Rethinking identity security in the agentic AI age

Identity security conversations often arrive at the same unfortunate scenario: a stolen token and breach only discovered once major damage is done. Experts Rob Kraczek, global strategist at One Identity, and Chris Ray, field CTO of security and risk at GigaOm, recently unpacked why 3 a.m. token theft has become less exception, more routine — among other things.

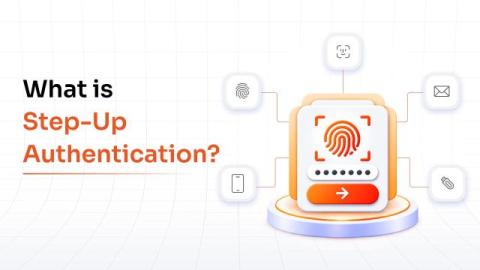
Step-Up Authentication: How It Works, Use Cases and Benefits

A user signs in to an application and gets access to the dashboard. Later, the same user tries to change account settings or approve a high-value transaction. Suddenly, another verification step appears. Why? The risk has changed. Routine access and sensitive actions do not need the same level of protection. Step-up authentication lets organizations add stronger verification when users cross a higher-risk threshold, while keeping everyday access simple.

Why academic selfie fraud benchmarks fail in the real world

Academic deepfake datasets rarely static: generate an image, label it real or fake, done. Real-world fraud doesn't hold still. Zhaofeng Si, a PhD student at University at Buffalo and research scientist intern at Persona, breaks down the gap. Public academic datasets are mostly typical face swaps and diffusion-model-generated images with a fixed label. In the real world, there's an attack-and-defense loop. Fraudsters actively probe for ways to bypass detection, so defenses have to keep adapting instead of training against a static benchmark.