Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

ERP and SIS Integration With IAM for Higher Educational Institutes

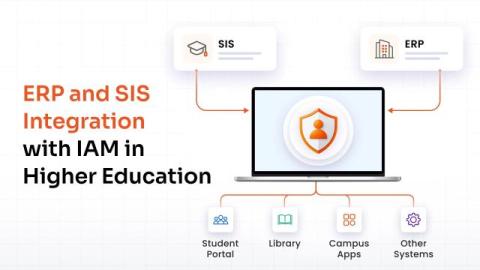
Higher education institutions manage identity information across systems such as Enterprise Resource Planning (ERP) platforms, Student Information Systems (SIS), and HR systems. These records determine whether someone is a student, employee, faculty member, researcher, alumnus, or another type of campus user. Integrating these systems with Identity and Access Management (IAM) lets institutions use those records to manage digital identities and access throughout the user lifecycle.
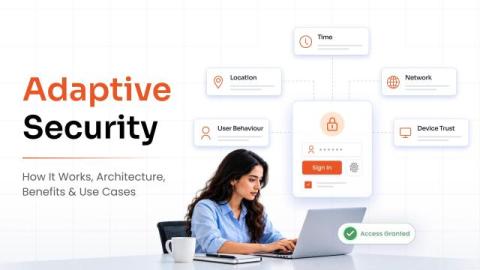
Adaptive Security: How It Works, Architecture, Benefits & Use Cases

Adaptive security is a cybersecurity approach that continuously monitors users, devices, networks, and security events to identify risks and adjust defenses in real time. Unlike static security models that rely on fixed rules and periodic updates, adaptive security responds to changes in behavior, context, and threat levels as they occur. It continuously evaluates security risks, detects unusual or suspicious activity, and adapts security controls based on the situation.

Apono Brings Just-in-Time Access to AWS IAM Account Access Manager

AWS just shipped AWS IAM Account Access Manager (AAM), a new way to grant AWS access through AWS IAM Identity Center using IAM roles. Apono is supporting AAM from day one, bringing just-in-time provisioning directly to the IAM roles your teams already trust. If you’re running AWS IAM Identity Center today, you’re likely provisioning access through permission sets.

Persona Research investigates big questions in online identity

Persona Research studies identity and trust. We advance methods for making online identity verification safer, fairer, and more accurate. We think this work is important because identity is fundamental to how people access services, form communities, and participate online. And we want to protect people without limiting their agency or access. Timestamps: Read more about Persona's research team, publications, and grant program: research.withpersona.com.

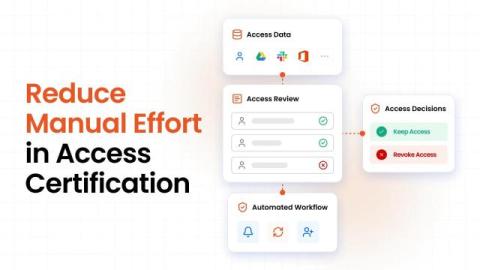
How to Reduce Manual Effort in Access Certification

Access certification can take more time than the actual review. A manager may need to review access for 50 employees. Before that happens, someone has to gather the access data, identify the right reviewer, send the requests, and track the responses. If the reviewer revokes access, someone may also need to remove it from the application. Now repeat that across hundreds of users and several applications. The workload adds up quickly.

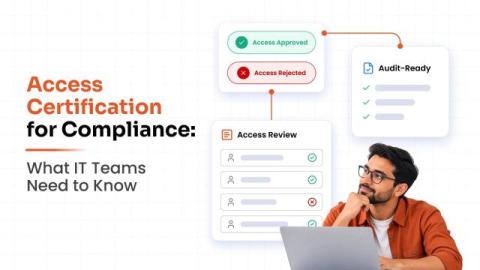
Access Certification For Compliance: What IT Teams Need To Know

An access review can look complete on paper. The campaign closed, reviewers made their decisions, and the records were saved. Then an auditor asks: Who reviewed this access, what did they decide, and what happened afterward? That question can reveal problems that a completed review does not show. A rejected permission may still be active. An exception may have no clear reason. The team may also struggle to show when the review happened.

Non-Human Identity Management in Atlassian Cloud

Ask a security team how many employees they have and they will answer instantly. Ask how many non-human identities they have, and the room goes quiet. Non-human identities (NHIs) are the identities that applications, services and automation use to act in a system. Service accounts, automation users and bot logins are identities, while API tokens, keys and certificates are the credentials they authenticate with, and teams have to govern both. These identities run deployments, sync data, post notifications and generate reports, usually without anyone watching.

MDM Implementation Checklist: From Planning to Deployment

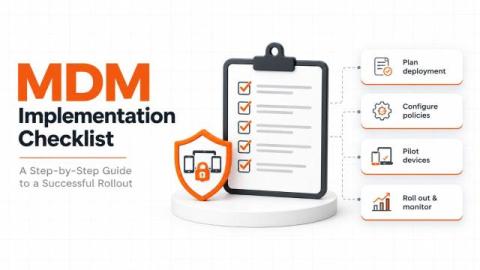
Enrolling devices is only one part of implementing Mobile Device Management (MDM). Before rollout, IT teams need to define ownership models, prepare the environment, configure policies, and verify that employees can access the apps and resources they need. This MDM implementation checklist breaks the process into seven phases, from initial planning to ongoing device management. Use it to organize responsibilities, identify dependencies, and confirm that each phase is ready before moving to the next.

Hybrid Identity Management: Secure Access Across Cloud and On-Premises

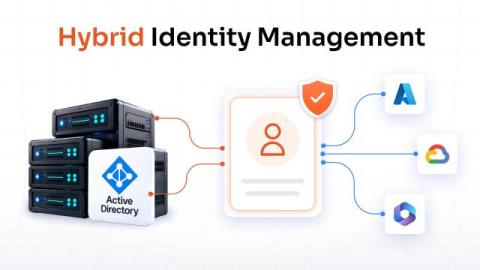
Hybrid identity management is the practice of managing user identities and access across on-premises and cloud environments through a connected identity framework. Most organizations today operate across both. Active Directory may still manage identities for internal applications, while cloud platforms and SaaS applications handle other parts of the business. This creates a simple challenge: how do you give users consistent access when their applications and identities exist in different environments?