Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Shadow AI: How Employees Leak Company Data Into AI Tools and How to Stop It

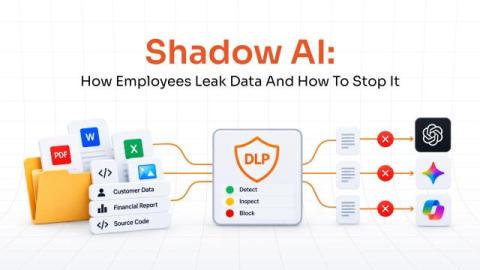
Shadow AI refers to the use of artificial intelligence tools, applications, models, or AI-powered features without the organization's required IT approval, security review, or governance. It is often associated with employees using personal accounts for tools such as ChatGPT or Gemini. However, Shadow AI extends well beyond public AI chatbots.
Passwordless Authentication Trends in 2027: What's Next for Login Security?

Passwords are no longer the only weakness in digital identity. Passkeys and FIDO2 reduce reliance on reusable credentials, but attackers can still target account recovery, steal active sessions, or exploit permissions granted to automated systems. Therefore, the next phase of passwordless authentication must address these gaps without making everyday access unnecessarily complicated.

What is OAuth (Open Authorization)?

OAuth (Open Authorization) is an open-standard authorization framework that allows applications to access an end user's protected resources without requiring the user to share their password. Instead, users grant applications limited access to specific resources through authorization, while their credentials remain private. OAuth uses access tokens to control what an application can access on a user's behalf.

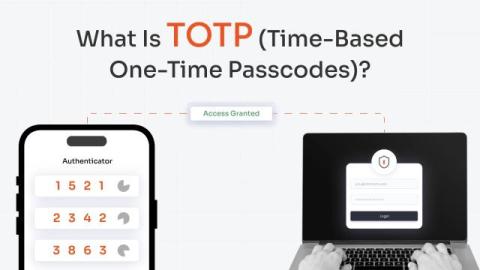
What Is TOTP? Security, Implementation, and Best Practices

TOTP (Time-Based One-Time Password) is an authentication algorithm that generates a unique, temporary numeric code using the current time as a moving factor. Typically, these codes are six digits long and automatically change every 30 seconds, providing a one-time verification code for authentication. TOTP uses a shared secret between the authentication service and the user's authenticator device, combining that secret with the current time to generate each code.

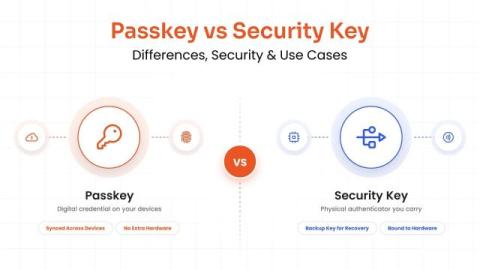
Passkey vs Security Key: Differences, Security & Use Cases

Passkeys and security keys both support phishing-resistant authentication, but they differ in how credentials are stored, managed, and used. A passkey is a digital authentication credential, while a security key is a physical authenticator that can store credentials and prove a user's identity. For enterprises replacing passwords, the distinction affects credential portability, recovery, hardware requirements, and control over authentication.

Q&A between researchers who are improving deepfake detection

In the real world, attackers don't just generate a selfie, submit it, and move on. If one attempt fails, they’ll refine the image and try again. Existing datasets often fail to account for these variations, leading the researchers’ detection models to fall short in real-world scenarios. Zhaofeng Si, a PhD student at University at Buffalo who interned at Persona as a research scientist, and Saatvik Billa, an ML engineer and researcher at Persona, worked together this summer on a fraud taxonomy and a real-world selfie fraud benchmark.

What Are Machine Identities?

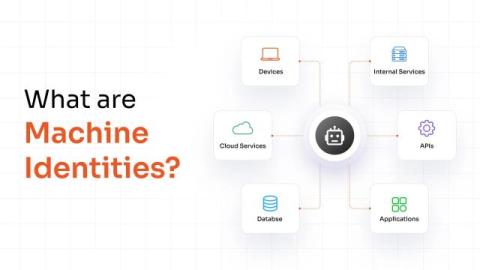
A machine identity is the set of credentials a non-human entity, such as an application, device, workload, or service, uses to authenticate itself and communicate securely with other systems. Just as an employee proves who they are with a username and password, a machine proves who it is with cryptographic credentials like a digital certificate, an API key, or a service account token.

What Is Remote Desktop Protocol (RDP)?

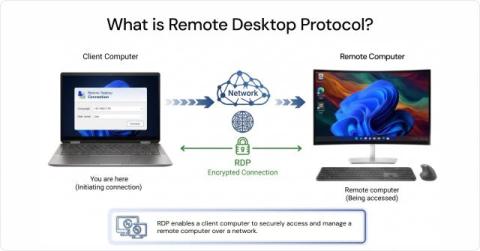
A field employee's laptop crashes, or a server in another office needs a patch, or a remote worker gets locked out of their workstation. For all these situations, the IT team needs to get in, fix it, and move on, without being there. Remote Desktop Protocol (RDP) is Microsoft's answer to that problem. It's a network protocol that lets you connect to another computer over a network and control it as if you were sitting right in front of it.