Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How to Automate Repository Backups to Minimize Data Loss and Downtime

In modern CI/CD pipelines, source code moves fast, and repository state changes constantly. Manual backups are inherently fragmented, error-prone, and incapable of capturing platform metadata at scale. To prevent critical data loss and ensure rapid failover, engineering teams must automate their repository backups.
The AI Incident Reporting Duty Nobody Can Date

Compliance content answers the question of when an obligation starts. For the serious incident reporting duty in the AI Act, the honest answer is that it is disputed, and the dispute is not a failure of research. ‍ Two readings of the text point in different directions, neither is obviously wrong, and no authority has resolved it. What follows is the reasoning on both sides and what to do without picking one. ‍

Cyber Loss When the Inventory Itself Perishes

An outage is normally modeled as deferred revenue. Production stops, orders wait, operations resume and some of the backlog is recovered by running longer. ‍ Where the inventory perishes, none of that applies. The stock is destroyed during the incident, restoring the systems does not bring it back, and running longer afterward produces new product rather than recovering the old. ‍

What's taking DNS-PERSIST-01 so long?

In February, Let’s Encrypt announced that DNS-PERSIST-01 was coming, “some time in Q2 2026.” It’s October, and it’s nowhere close to ready. We’ve been waiting for DNS-PERSIST-01 since January, along with every other ACME client and lots of organizations. DNS-PERSIST-01 promised to simplify domain validation and make automation easier, but we had to wait on Let’s Encrypt. Let’s Encrypt is waiting on a redesign, a standards body, and maybe one more vote.

Step-Up Authentication: How It Works, Use Cases and Benefits

A user signs in to an application and gets access to the dashboard. Later, the same user tries to change account settings or approve a high-value transaction. Suddenly, another verification step appears. Why? The risk has changed. Routine access and sensitive actions do not need the same level of protection. Step-up authentication lets organizations add stronger verification when users cross a higher-risk threshold, while keeping everyday access simple.

Beyond Renew or Replatform: A Fourth Option for VMware Customers

A customer tells you they want off VMware. They have seen the headlines, looked at the latest renewal, and decided it is time to evaluate Nutanix, Proxmox, public cloud, or another virtualization platform. The opportunity appears straightforward: help them select an alternative and build the migration plan. But what if leaving VMware isn’t actually the best answer? A platform move is risky, time-consuming, and expensive.

State of Application Security

Our View from the Front Lines of Technical Assessments Kroll analyzed five years of penetration testing data. Of the trends that emerged, we focus on three in this report: the static application security testing (SAST)/software composition analysis (SCA) plateau, the need for more attention around authentication and authorization, and the security health divergence, which shows that regulation is not a reliable predictor of attack surface health.

Meta Muse in the Enterprise: Data Security for Personal Autonomous Agents

The deployment of personal AI agents like Meta's Muse represents a structural shift in enterprise data loss prevention. Unlike conversational web chatbots where data movement is limited to manual user prompts, autonomous personal agents operate in cloud virtual machines, run continuous background tasks, and connect directly to enterprise SaaS platforms through OAuth integrations.

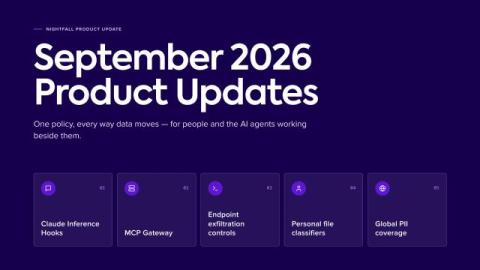
September 2026 Product Updates

September was the month Nightfall's control layer reached inside the model call. Five releases shipped: Claude Inference Hooks, MCP Gateway, expanded endpoint exfiltration controls, personal file classifiers, and PII coverage across 30 countries. Together they close the gap between what security teams can control when a person moves data and what they can control when an AI agent does.