Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

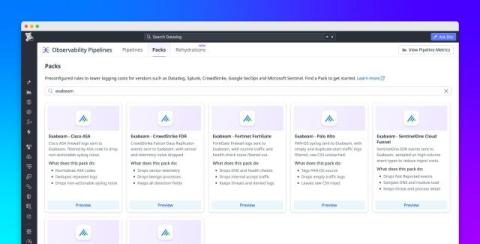
Process and route critical security logs to Exabeam with Observability Pipelines

Enterprise security teams use Exabeam as a security information and event management (SIEM) platform with user and entity behavior analytics (UEBA) to detect insider threats, lateral movement, privilege escalation, credential compromise, and data exfiltration.
How Essential Eight impacts government contracting in Australia

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Falcon Data Security for SaaS Secures Sensitive Data in Microsoft 365

For many organizations, Microsoft 365 environments are essential to data security strategy. Their strategic plans live in SharePoint; their employee records and customer data are stored in OneDrive. Teams use these tools to collaborate on projects every day, and increasingly, AI tools like Microsoft Copilot can access the information they rely on.

New in Falcon Cloud Security: Third-Party App Insights and AI-Enhanced Remediation

Two forces are reshaping modern cloud posture management: context and AI. Context gives security teams the business insight to understand risk. AI helps them turn that insight into faster, more informed action. CrowdStrike Falcon Cloud Security is advancing both. New third-party application insights map the external services cloud-native applications depend on, helping customers assess the risk those dependencies introduce.

EU Cyber Resilience Act: Europe Just Put Your AI Agents on a 24-Hour Clock

In short, the EU Cyber Resilience Act (CRA) puts binding cybersecurity requirements on any software sold as a product in the EU, and it does not carve out AI agents. Since 11th September 2026, any company that sells software with digital elements into the EU has 24 hours from learning that a vulnerability is being exploited to file an early warning with a national CSIRT and ENISA, 72 hours to describe it, and 14 days to report what it did about it.

Exfiltration Vectors Compound. Your Protection Has to as Well.

AI didn't replace the old ways data leaves a company. It added new methods on top and gave insiders a way to chain them together. You only see the chain if one sensor watches humans and AI together. If you spend enough time around CISOs / data security/ insider risk practitioners who have run these program for a decade you won't hear that AI is the only thing that matters.

Privileged user monitoring: Visibility without trust

Operations require elevated access and organizations grant it on trust, so privileged user monitoring has to turn that trust into evidence. An authorization record shows only that the system permitted an action. Monitoring produces a reviewable account of which elevated rights each person used and when, which lets an auditor or investigator test activity without disrupting administration.

Emerging Threat: (CVE-2026-94483) Next.js Server-Side Request Forgery via Image Optimization

CVE-2026-94483 is a server-side request forgery flaw in the Image Optimization feature of Next.js, the React framework maintained by Vercel. It is classified as CWE-918. Image Optimization fetches a remote image on the server and re-encodes it. Before fetching, it checks the requested URL against the images.remotePatterns allow-list. The flaw is that the allow-list check and the fetch resolve DNS separately, so a host that passes the check can resolve to a different address by the time the fetch happens.

Revoked Isn't Removed: The Supplier Exposure a Federal Ban Leaves Behind

Federal security restrictions and procurement bans have targeted Chinese telecommunications and technology suppliers for years. But removing a company's name from an authorization is not the same as removing the risk it carries into a supply chain. For C-SCRM programs, the harder question is identifying where that risk persists — through affiliates, resellers, data center tenancies, and proxy or sub-tier relationships that no order directly names.

Put Threat Intelligence to Work

Threat intelligence is easy to find. Turning it into a detection that works in your environment is harder. A new campaign surfaces. Research lands in an inbox, threat feed, or repository. Then the real work starts. Someone has to identify the behaviors worth detecting, find the right telemetry, map the right attributes, build the logic, validate it, and tune it for the environment. That work takes expertise. And in many SOCs, that expertise sits with a small number of detection engineers.