Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Outsourcing Government Services: Essential Guide for Local Governments

Local governments often face the challenge of delivering quality services amidst budget constraints and increasing public demands. Outsourcing Government Services offers a strategic solution to enhance efficiency and reduce costs. However, the process of outsourcing requires careful consideration and planning to ensure it aligns with public expectations and regulatory requirements. This guide explores essential strategies, suitable services, potential challenges, and best practices for successful outsourcing initiatives, specifically tailored for local governments.
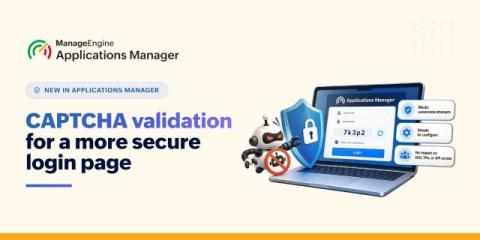
Protect Applications Manager logins with CAPTCHA validation

Login pages are one of the most attacked surfaces of any enterprise tool. They're often internet-facing, they're the front door to sensitive operational data, and unlike most vulnerabilities, they don't need to be discovered—they can simply be targeted with large volumes of automated attempts. For monitoring platforms like Applications Manager, which frequently sit with visibility into critical infrastructure, that front door matters even more.

A Simpler Way We Release and Support Every Product

A plain-language look at our new release and support policy — and what it means for you, no matter which product you run. For customers and partners, release and support practices have not always been easy to interpret. Different products used different terms for similar things — major and minor releases, patch releases, hotfixes — which made it hard to know which release to adopt, how long it would be supported, or whether a given update added functionality or only fixed something.

Rethinking identity security in the agentic AI age

Identity security conversations often arrive at the same unfortunate scenario: a stolen token and breach only discovered once major damage is done. Experts Rob Kraczek, global strategist at One Identity, and Chris Ray, field CTO of security and risk at GigaOm, recently unpacked why 3 a.m. token theft has become less exception, more routine — among other things.

Citrix NetScaler vulnerability (CVE-2026-88779) in active exploitation

On October 4, 2026, Citrix disclosed a high-severity (CVSS score of 8.7) memory overflow vulnerability (CVE-2026-88779) affecting Citrix NetScaler ADC and Citrix NetScaler Gateway deployments that are configured as either a SAML Service Provider (SP) or SAML Identity Provider (IdP). Successful exploitation can cause a denial of service (DoS) condition, potentially disrupting authentication services and remote access functionality.

Insider risk starts with who can read the data

Insider risk is often framed as an external attacker problem, but a real blind spot sits closer to home: who inside your own security stack can open sensitive files they never needed to see. Classification tools that require broad scanning access often hand that same access to every admin who configures them, turning the tool meant to reduce exposure into another path to it. The people with the least oversight, your own admins, can end up with the most unchecked visibility into regulated data.

Convergence of ITDR, PAM and IGA. Which of the three is standing there when the attack lands?

Our 2026 Identity and Data Security Report put compromised identity ahead of misconfigured permissions as the leading route to unauthorized access, 41.8% against 33.9%. If identity is the way in, the controls around identity belong together, and that's the reasoning behind most of the consolidation we've seen over the past few years. But how is the work split up?

The Egnyte + Procore Integration: Connecting Project Execution with Construction Knowledge

Construction firms rely on purpose-built platforms like Procore to coordinate RFIs and submittals, document field activity, track progress, and keep projects on schedule. But managing project execution is only one part of the information lifecycle—teams need a way to capture and connect project information across departments, applications, partners, and project phases.

[Cybersecurity Awareness Month] Cyber Espionage: When the Attacker's Best Asset Is You

Spies have always relied on technology, disguises, secret communications and clever gadgets, at least if the movies are to be believed. But some of the most effective tools in the espionage business have always been people. Convince the right person to open a door, reveal a secret or trust someone they should not, and suddenly bypassing the sophisticated security system becomes unnecessary.

Threat Actors Abuse Trusted Accounts and Internal Tools to Launch Convincing BEC Attacks

Attackers are continually finding new ways to refine business email compromise (BEC) attacks, according to Douglas McKee, Director of Vulnerability Intelligence at Rapid7. When attackers compromise trusted tools and accounts, they can manipulate victims’ view of reality. One way attackers can achieve this is through what McKee calls “calendar warfare,” in which attackers use calendar meetings to trick users into falling for attacks.