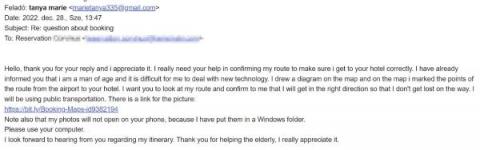
Since late December 2022, the ThreatSpike team has noticed a significant rise in highly targeted phishing campaigns aimed at the hospitality sector, which distribute infostealer malware. The threat actors (TAs) are primarily targeting front desk and reception staff, as they are responsible for handling customer queries via a generic email that can easily be found on the company website.
In a world where you can scan the veins in your hand to unlock a smartphone, how do you maintain control over personal data? Biometric authentication, the use of distinctive human features like iris patterns, fingerprints and even gait in lieu of a password, is gaining ground in the tech world. Proponents tout its inherent, hard-to-replicate qualities as a security benefit, while detractors see the same features as an invasion of privacy. Both sides may be right.
Finance Minister Nirmala Sitharaman advocated for the simplification of Know Your Customer (KYC) processes for financial services in a Budget speech that placed a broad emphasis on technology and tech-driven solutions. She also argued for increasing the utility of the DigiLocker platform for both individuals and businesses and giving Fintech Platforms more flexibility to access India’s digital infrastructure.
‘Can I trust a password manager that stores my data in the cloud?'
So far in this series, we’ve looked at the importance of securing an organization’s network, application components, and the endpoints that support them. In this post, we’ll look at the following best practices for protecting the different types of data that flow through these components. But first, we’ll look at how modern applications process and manage data, as well as common weaknesses and security threats to these systems.
The compromise of a single Active Directory credential can lead to unauthorized access to your servers, applications, virtualization platforms and user files across your enterprise. One of the reasons for credential vulnerability is that Windows stores credentials in the Local Security Authority (LSA), which is a process in memory.
Microsoft recently updated its guidance for how organizations should approach privileged access in Active Directory (AD). A key component is shifting from the tiered access model (TAM) and the Enhanced Security Admin Environment (ESAE) (also known as the Active Directory Red Forest) to the Enterprise Access Model (EAM). This article explains the drawbacks of the older models and the key principles of EAM.
NITDA launched the ground-breaking Nigeria Data Protection Regulation (NDPR) in early 2019, cementing a culture of data privacy and protection for all Nigerians. By mirroring Europe's GDPR Framework, NITDA demonstrated its commitment to safeguarding citizens' online security. Private organizations, such as mobile development companies that control or process data, must comply with this regulation to stay operational. Fortunately, we're here to help you avoid any costly missteps.