
San Mateo, CA, USA
2007
  |  By LevelBlue
Security leaders across Asia/Pacific are being asked to do more than watch alerts. Boards and regulators want proof that the organization can withstand an attack, contain it fast and recover with minimal disruption. That shift, from managed security to cyber resilience, is reshaping what organizations need from a security partner.
  |  By Brad Schonhorst
Managed Security Services can give security teams greater visibility and access to specialized expertise, but finding a threat is only one part of incident response. Once an alert becomes an incident, the operating model between an internal security team and its managed security service provider (MSSP) becomes critical.
  |  By LevelBlue
Cyber insurance has traditionally done its most important work after something goes wrong. We think it can do much more before an incident ever happens. That's why LevelBlue is partnering with rrelentless, a UK-based specialist Managing General Agent (MGA), to give its cyber insurance policyholders access to LevelBlue's cybersecurity expertise as part of their policy.
  |  By Nolen Johnson
Overnight on November 2, freezers in supermarkets across Sweden, Belgium, Luxembourg and Ireland climbed to around 50°C, and stores awoke to spoiled stock. This is the second wave within a month, after a similar attack on hundreds of French stores in October. No one has publicly claimed either attack, and the attack vector hasn't been confirmed. Regardless of who is responsible, the targets are what should worry us.
  |  By LevelBlue
LevelBlue has been named Editor's Choice for Managed Detection and Response (MDR) in Cyber Defense Magazine's Top InfoSec Innovators awards for 2026. The award was announced on October 20, 2026, during CyberDefenseCon 2026 in Orlando, Florida. It's a recognition we're especially proud of. MDR sits at the heart of what LevelBlue does every day: helping organizations detect threats faster, respond with confidence, and stay one step ahead of attackers.
  |  By Grant Hutchons
Why a Five Eyes follow-the-sun Security Operations Centre delivers better outcomes than a local SOC with a pager, and how to tell which one you are really buying.
  |  By LevelBlue
Originally published by the PGA of America. Operating a golf facility means keeping track of a lot more than what’s happening on the course. Tee times, lesson schedules, payroll and vendor payments all depend on technology working as it should. Keeping those systems secure is easy to put off when everything is running smoothly, but it’s worth making time before a problem interrupts the day.
  |  By Colin Henderson
LevelBlue’s free Zero Trust Readiness Review helps organizations uncover security gaps and get more value from their existing investments. One of the first questions I ask security leaders is simple: Do you know whether all your security tools work together? The answer is rarely a straightforward yes. Most organizations have built their security environments over many years.
  |  By LevelBlue
Today, SentinelOne named LevelBlue its global exclusive delivery partner for Wayfinder, SentinelOne’s suite of AI-powered managed security and threat detection services. LevelBlue will deliver Wayfinder managed detection and response (MDR), threat hunting, incident readiness and response (IRR), and SentinelOne’s professional services for organizations around the world. It’s a milestone for our teams, and it reflects something we believe deeply about security in the AI era.
  |  By LevelBlue
Three LevelBlue security experts put their investigative skills to the test in the SentinelOne Threat Hunting competition, with Jodie McDonald earning the top spot in EMEA and advancing to the Grand Final at OneCon. Threat hunting requires more than knowing your way around a security platform. It takes curiosity, analytical thinking, and the discipline to follow the evidence, even when it leads somewhere unexpected.
  |  By LevelBlue
Many organizations that have historically been managing their security and network strategies independently from one another are looking to simplify and integrate their solution into a unified solution. In this instance, the value of a SASE solution is clear - but rolling out an effective implementation can be a challenge. This is where an MSSP can step in and provide the expertise to outline a proven strategy to move into a SASE solution that meets the customer where they are.
  |  By LevelBlue
As API usage surges and application environments evolve, organizations are increasingly relying on a mix of WAFs, DDoS protection, API security, and bot management tools, often from different vendors. While many have coverage across key areas, this fragmented approach leads to what we call WAAP sprawl: multiple tools, multiple vendors, and increased complexity. Can organizations effectively manage all of this?
  |  By LevelBlue
Many companies have an incident response retainer...but it doesn't actually make them risk ready. That's because too many retainers are built on outdated, hour-based "use it or lose it" models that don't actually reduce risk, improve resilience, or focus on outcomes. A modern retainer should drive preparedness, align with today's insurance realities, and actively lower exposure before an incident happens.
  |  By LevelBlue
Some of the biggest delays in incident response aren’t caused by the attacker… they’re caused by the first steps taken after discovery. A few examples of well-intentioned actions that can unintentionally slow investigations and extend recovery timelines: Resilience isn’t built during an incident. It’s built before one ever happens.
  |  By LevelBlue
LevelBlue. Built for what’s next. AI-powered security that stays ahead of threats, not reacts to them. From cloud to network to hybrid, we deliver total visibility, total control, and protection at scale, so enterprises can move faster with confidence.
  |  By LevelBlue
Originally recorded in 2025, we look back at how cybercriminals perfected deception during the first half of the year. Now available as an archive recording, the session highlights the second edition of the LevelBlue Threat Trends Report and explores real-world incident data, fast-moving attack chains, and the social engineering techniques that shaped the threat landscape at the time. While the data reflects early 2025, many of the lessons remain relevant for understanding how today’s threat environment evolved.
  |  By LevelBlue
Originally recorded in 2025, we look back at the key threat trends and attack techniques shaping the security landscape at the time. Now available as an archive recording, the session explores emerging threats, evolving attacker tactics, and early indicators of risks that still influence cybersecurity strategies today. While the data reflects 2025, many of the insights remain relevant for understanding how the modern threat landscape has evolved.
  |  By LevelBlue
LevelBlue and the PGA of America share a commitment to excellence under pressure. As the Official Cybersecurity Advisor of the PGA of America, LevelBlue brings championship standards of protection, continuity, and trust to the organizations that keep the game - and business - moving forward. From fairways to firewalls, LevelBlue safeguards mission-critical operations, member data, and high-profile events with always-on defense, accelerated response, and expert-led security operations powered by AI-driven threat intelligence.
  |  By LevelBlue
Cyberattacks are evolving fast; powered by AI, deepfakes, ransomware, phishing, and growing software supply chain risk. So how prepared is your organization? In this webcast, we breakdown key findings from the 2025 LevelBlue Futures Report (in partnership with FT Longitude). The report is based on a global survey of 1,500 C-suite and senior executives across 16 countries and seven industries, including healthcare, financial services, energy, and manufacturing.
  |  By LevelBlue
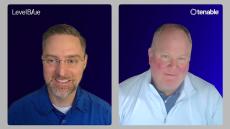
Discover how LevelBlue and Tenable are transforming cybersecurity in this exclusive fireside chat featuring Michael Vaughn, Director of Product Management at LevelBlue, and Greg Goetz, VP of Global Strategic Partners at Tenable.
  |  By LevelBlue
Phenomenal security. Phenomenal partnership. At AlienVault, we understand that customers rely on your expertise to deliver world-class security solutions specifically designed to protect their unique business. We also know that vetting partnerships opportunities with security vendors is a critical component to delivering those outcomes.
  |  By LevelBlue
The Insider's Guide to Incident Response gives you an in-depth look at the fundamental strategies of efficient and effective incident response for security teams that need to do more with less in today's rapidly changing threat landscape.
  |  By LevelBlue
As organizations around the world shift their workloads to Amazon Web Services (AWS) and other popular cloud infrastructure-as-a-service (IaaS) providers, concerns about cloud security continue to rise. According to a 2018 Cloud Security Report from Cybersecurity Insiders, 91% of respondents are concerned about cloud security, an increase of 11% over last year's report.
  |  By LevelBlue
Get All 5 Chapters of AlienVault's How to Build a Security Operations Center (On a Budget) in 1 eBook! You'll get an in-depth look at how organizations with limited resources can set up a successful operations center for monitoring, detecting, containing, and remediating IT threats across applications, devices, systems, networks, and locations.
  |  By LevelBlue
Criminal organizations and hackers increasingly perceive regional banks and credit unions as attractive targets. That's why we've created this primer-to help IT managers and executives at financial organizations understand not just the top threats they're facing, but also what they can do to fend them off.
  |  By LevelBlue
This whitepaper provides an overview of Open Source IDS and the various IDS tools available today. Whether you need to monitor hosts or the networks connecting them to identify the latest threats, these are some of the best open source intrusion detection (IDS) tools available to you.
  |  By LevelBlue
With so many open source tools available to help with network security, it can be tricky to figure out where to start, especially if you are an IT generalist who has been tasked with security.

LevelBlue has simplified the way organizations detect and respond to today’s ever evolving threat landscape. Our unique and award-winning approach, trusted by thousands of customers, combines the essential security controls of our all-in-one platform, AlienVault Unified Security Management, with the power of AlienVault’s Open Threat Exchange, the world’s largest crowd-sourced threat intelligence community, making effective and affordable threat detection attainable for resource-constrained IT teams.

AlienVault® USM Anywhere™ accelerates and centralizes threat detection, incident response, and compliance management for your cloud, on-premises, and hybrid environments. USM Anywhere includes purpose-built cloud sensors that natively monitor your Amazon Web Services (AWS) and Microsoft Azure cloud environments, and cloud applications like Office 365. On premises, lightweight virtual sensors run on Microsoft Hyper-V and VMware ESXi to monitor your virtual private cloud and physical IT infrastructure.

With USM Anywhere, you can rapidly deploy sensors into your cloud and on-premises environments while centrally managing data collection, security analysis, and threat detection from the AlienVault Secure Cloud.