Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Secure by default: recommendations from the CISA's newest guide, and how Cloudflare follows these principles to keep you secure

When you buy a new house, you shouldn’t have to worry that everyone in the city can unlock your front door with a universal key before you change the lock. You also shouldn’t have to walk around the house with a screwdriver and tighten the window locks and back door so that intruders can’t pry them open.
Microsoft 365 Security Series - Using Azure Active Directory to secure your Microsoft 365 Installation

Microsoft 365 (formerly Office 365) is a Software-as-a-Service (SaaS) that offers a cloud-based version of its popular software productivity suite, including MS Word, Excel, PowerPoint, Outlook, and OneNote. In contrast, Azure Active Directory (Azure AD) is an Infrastructure-as-a-Service (IaaS) that offers a cloud-based version of Active Directory to control identity management and access to virtual resources across an organization.

Securing private applications with CrowdStrike Zero Trust Assessment and AWS Verified Access

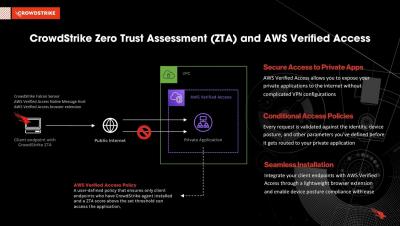
CrowdStrike Zero Trust Assessment (CrowdStrike ZTA) provides customers the ability to assess their endpoint security posture, allowing AWS Verified Access to provide conditional access to resources that comply with their organization’s device posture policies.

Securing private applications with CrowdStrike Zero Trust Assessment and AWS Verified Access

AWS Verified Access (AVA), a feature of Amazon Virtual Private Cloud (VPC) networking, delivers secure, zero-trust access to private applications without a VPN by continuously evaluating each request in real time based on contextual security signals like identity, device security status and location. The service grants access based on the security policy configured for each application and then connects the users, thereby improving the security posture of the organization.

The 443 Podcast, Ep. 236 - Another Software Supply Chain Attack

This week on The 443, Corey Nachreiner and Marc Laliberte discuss the latest software supply chain attack with a potential blast radius of thousands of organizations. They then cover a new protocol vulnerability in the Wi-Fi wireless standard before ending with some research into insecure Microsoft Azure applications.

Mend.io Achieves AWS Security Competency Status

We’re delighted to announce that Mend.io has achieved Amazon Web Services (AWS) Security Competency status. This designation recognizes that Mend.io has demonstrated proven technology and deep expertise to help customers achieve cloud security goals. It reinforces Mend.io’s position as a trusted member of the AWS Partner Network (APN), which has already been established since we achieved AWS DevOps Competency status.

Securing private applications with CrowdStrike and AWS Verified Access

CrowdStrike Zero Trust Assessment (CrowdStrike ZTA) provides customers the ability to assess their endpoint security posture, allowing AWS Verified Access to provide conditional access to resources that comply with their organization’s device posture policies.

Effective AWS Incident Response: Examples and Recommendations

The use of Amazon Web Services (AWS) in organizations around the world is prolific. The platform accounted for 31% of total cloud infrastructure services spend in Q2 2022, growing by 33% annually. Despite its widespread use, many organizations still fail to consider the nuances of incident response in AWS.

Best practices for identity and access management in cloud-native infrastructure

Editor’s note: This is the final part of a five-part cloud security series that covers protecting an organization’s network perimeter, endpoints, application code, sensitive data, and service and user accounts from threats. So far in this series, we’ve looked at the importance of securing an organization’s network, its application components, the endpoints that support those components, and its application data.

Cloud forensics - An introduction to investigating security incidents in AWS, Azure and GCP

The cloud has revolutionized the way we do business. It has made it possible for us to store and access data from anywhere in the world, and it has also made it possible for us to scale our businesses up or down as needed. However, the cloud also brings with it new challenges. One of the biggest challenges is just keeping track of all of the data that is stored in the cloud. This can make it difficult to identify and respond to security incidents.