Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Red Teaming Agentic AI: Why Testing the Model Is No Longer Enough

In January 2025, NIST's Center for AI Standards and Innovation published red team results that should have changed how enterprises test autonomous systems. Against an AI agent operating in simulated workspace, travel, Slack and banking environments, the strongest previously known hijacking attack succeeded 11% of the time. The strongest new attack developed by the red team succeeded 81% of the time. The model had not changed. The evaluation had.

Ranked: The 10 Best AI SEO Agencies for 2026

SEO is having a bit of a moment. Getting onto page one of Google still matters, of course, but that is no longer the whole picture. Brands now also need to think about whether they are being mentioned in AI-generated answers, summaries, recommendations, and conversational search results. That is where AI SEO comes in. The strongest agencies in 2026 are not throwing traditional SEO out the window. They are combining the fundamentals that still work with newer strategies built around AI search visibility, authority, brand mentions, and genuinely useful content.

Devil's advocate? Uncensored Luciferus AI service advertised underground

On August 24, 2026, Counter Threat Unit (CTU) researchers observed an Exploit underground forum persona named “Optimus_Prime” advertising an uncensored AI subscription service named Luciferus. The persona joined Exploit on April 18, and their profile displays a “coding / coder” activity label. As of September 4, the persona has published 21 posts on the forum.

Does an agent have more access than you do?

70% of organizations give AI more access than a human in the same role would get. Not surprising when it is common for a team to click “always” when an agent asks to be allowed once or always allowed. That means the agent holds that access in perpetuity and turns into agent over-provisioning. Makes you wonder: Does an agent have more access to your organization's stack than it should and more access than the people who deploy them?

Introducing Guardian Agents: Meet Blue Agent, Your AI Security Analyst

AI agents are moving into production faster than security teams can govern them. And unlike traditional applications, agents continuously make decisions, invoke tools, access data, and take actions. Every one of those interactions creates security context that needs to be understood. At enterprise scale, asking analysts to manually evaluate every finding becomes impossible.

Warning: "Slop Squatting" Directs AI Users to Phishing Pages

Threat actors are increasingly leveraging AI hallucinations to plant phishing links and other malicious content in AI output, IEEE Spectrum reports. Large language models (LLMs) sometimes fabricate information, including web domains, when answering users’ questions. Attackers are registering these hallucinated web domains to host phishing pages.

Evidence for One AI Framework Does Not Count for the Next

An organization assembles an evidence package for one AI framework, passes, and discovers that almost none of it transfers to the next instrument applying to the same system. The frameworks agree on the principles and disagree on what proves them. Three frameworks defining risk differently is the same problem one layer earlier. ‍ The common response is to look for a crosswalk and treat the mapping as a reuse plan.

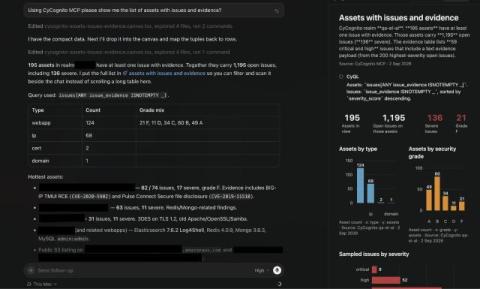
Introducing the CyCognito MCP Server: Full Exposure Context, On Demand

Today we are happy to announce the beta release of the CyCognito MCP server, which makes your external attack surface data consumable by any AI client that speaks the Model Context Protocol, including Claude, Cursor, and ChatGPT. The server runs on CyQL, the proprietary query language behind advanced search in our platform. CyQL is designed to ask precise questions about an attack surface, using operators suited to each type of asset, issue, and relationship.

AI Agent Security Readiness: The Federal Standard You Should Get Ahead Of

Here's the uncomfortable part first: in August 2026, researchers found AI agents connected to Hugging Face running loose inside enterprise networks. No owner, no audit trail, nobody who could tell you they existed until something broke. If that sentence made your stomach drop a little, good, because it should. It's the same blind spot most security teams are sitting on right now. They just haven't had their version of the incident yet.

AI is learning to control machines...but can it trust them?

Anthropic’s new Model Hardware Standard (MHS) could mark an important step in the evolution of agentic AI. Currently in research preview, MHS provides a standardized way for AI agents to discover, understand and operate physical equipment. Anthropic is already demonstrating the concept with laboratory and manufacturing equipment including robotic arms, microscopes, liquid handlers and laser systems. The objective is compelling.