Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How to detect non-CVE vulnerabilities that standard scanners miss

If your application security program only tracks known Common Vulnerabilities and Exposures (CVEs), you’re probably missing a large share of your real risk. Across the Detectify platform, 75% of the vulnerabilities in our test catalog and 99% of those we discover in customers’ assets are non-CVE vulnerabilities. That makes public disclosures a poor measure of coverage on a modern attack surface. Below, we look at why so many vulnerabilities never get a CVE and how Detectify finds both kinds.
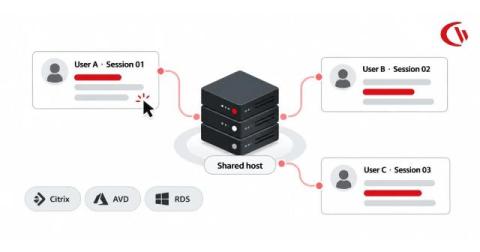
Multi-Session User Tracking in Citrix & Azure Virtual Desktop: Session-ID Mapping vs. Device Logging

In 2026, enterprise computing will be largely consolidated and centralized, and organizations will be shifting away from the one-user-per-PC model towards shared, multi-user virtualization technologies like AVD, Citrix Virtual Apps and Desktops, and Microsoft Remote Desktop Services (RDS).

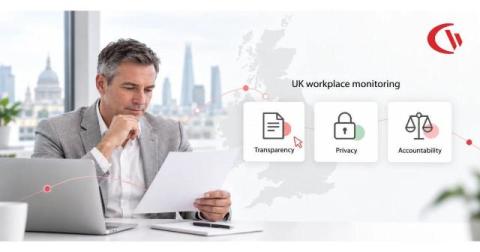
UK Employee & Workplace Monitoring Laws: The 2026 Employer Compliance Guide

In the UK, workplace monitoring rules are changing quickly as the Information Commissioner’s Office (ICO) releases new guidance following the passage of the Data (Use and Access) Act 2025. Since the Act came into effect, UK companies have had to comply with strict legal limitations on employee privacy because of the ICO’s guidance concerning work-related monitoring. What should be done to ensure that employee monitoring laws are valid?

GitProtect 2.5.0: Lightweight Replication, Microsoft Graph API Support, and Enhanced Restores

In the latest 2.5.0 release, we’ve improved copy replication to execute faster and use less resources. We also optimized Microsoft 365 backups with Graph API support, and made restore experience across multiple workloads smoother. Read on to learn about all enhancements in the 2.5.0 release of GitProtect.

Hunt or be Hunted: Every service was unique, and that was the problem

Stacking is usually the first thing we reach for on a persistence hunt. Pull every service, autorun or scheduled task across the environment, count how many endpoints have each one, and sort ascending. The entries at the bottom, the ones that show up on one or two machines, are where you start digging. In one Tanium Customer's environment, that didn't work at all. Each endpoint returned somewhere between a hundred and five hundred rows, and almost every one of them was unique to that endpoint.

How to handle privacy questions during enterprise security reviews

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

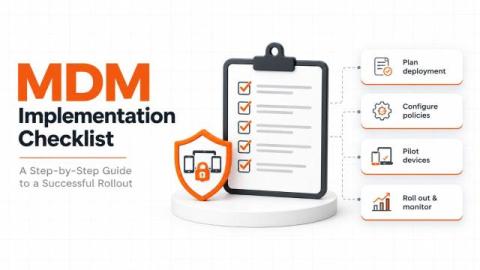
MDM Implementation Checklist: From Planning to Deployment

Enrolling devices is only one part of implementing Mobile Device Management (MDM). Before rollout, IT teams need to define ownership models, prepare the environment, configure policies, and verify that employees can access the apps and resources they need. This MDM implementation checklist breaks the process into seven phases, from initial planning to ongoing device management. Use it to organize responsibilities, identify dependencies, and confirm that each phase is ready before moving to the next.

Why Large File Workflows Break and How Media Teams Are Anchoring Control

In case you missed us, the Egnyte team was at NAB 2026 in Las Vegas. During a Tech Theater session, we dove deep into the mechanics of modern media workflows and why the traditional model of collaboration is reaching a breaking point. The conclusion? The industry has a problem that goes far deeper than just "large files are hard to move.".

[Cybersecurity Awareness Month] Trust, but Verify: Navigating the Era of AI Deepfakes

The digital landscape faces a new and complex challenge: the rise of generative AI. While these tools offer incredible potential for innovation, they also provide malicious actors with sophisticated ways to deceive even the most vigilant users.