Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Falcon Data Security for SaaS - Secure Sensitive Data in Microsoft 365

See CrowdStrike Falcon Data Security for SaaS in action and learn how to discover, classify, and protect sensitive data across Microsoft 365. See how security teams can identify sensitive data in SharePoint and OneDrive, prioritize exposure, automatically apply Microsoft Sensitivity Labels, reduce unintended Microsoft Copilot exposure, and extend protection with just-in-time access.
Calibrating a Cyber Loss Model to One Environment

A model built on industry data produces an industry answer. The obvious next step is to calibrate it to the specific environment, and the obvious place to start is the threat picture, because every organization believes its own is distinctive. ‍ It is the wrong parameter to start with. Some inputs should stay general, some must be local, and the ones that must be local are the harder ones to observe, which is why they get left at a default. ‍

Preparing for an ISO 42001 Audit Rather Than Reading About It

Plenty of material explains what ISO/IEC 42001 contains. Clause by clause, control by control, with a checklist of documents to prepare. The standard itself is a management system specification rather than a control catalogue, and the distinction is where audit preparation goes wrong. ‍ The checklists share one omission.

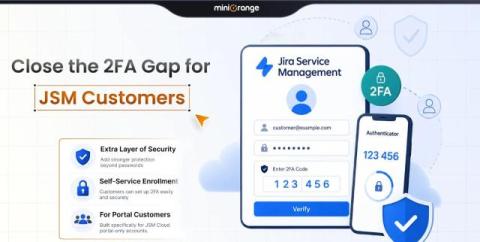
2FA for JSM Cloud Portal Customers: Closing the Gap Atlassian Guard Leaves Open

Atlassian Guard protects your employees through SSO and MFA. It does not cover portal-only customer accounts. However, customers need to access your Jira Service Management (JSM) portal to raise tickets and do so securely. But they often use portal-only accounts, which, in most cases, are protected only by a password. You’ll have security gaps if they don’t authenticate the same way as your employees. You must understand what the limits of Atlassian Guard are.

You Can't Secure the AWS Accounts You Don't Know About.

Ask an AWS security team how many accounts they run, and the honest answer is usually a range. Enterprises on AWS operate anywhere from 100 to 5,000 accounts. Most security teams can see only a fraction of them. That gap is why we built Wallarm Infrastructure Discovery. This week, it was named Enterprise Cloud Security Solution of the Year in the 10th annual CyberSecurity Breakthrough Awards. Here's what it does, and why the judges picked it.

How to write and enforce a removable media policy

Most organizations have a removable media policy. Few enforce one, and that shortfall drives breach costs and compliance exposure. Closing it takes a default-deny baseline, an approved-device register, encryption on everything you allow, expiring exceptions, and audit evidence proving each clause works. Writing a removable media policy takes an afternoon, and most organizations already have one covering USB drives and other portable storage.

What Are Unmanaged Data Stores and How to Secure Them

Unmanaged data stores let permissions drift while sensitive data accumulates unnoticed. They are repositories an organization doesn’t actively govern, leaving them without an owner, an access-review cadence, or a retention policy. Securing them means assigning ownership, correcting access, and maintaining continuous governance and visibility.

Zero Touch Patch Automation: Tanium Tech Talks #172

How do you patch faster - all while honoring your patching policies and *not* breaking things? Attackers are using AI to find and exploit vulnerabilities faster, and vendors are shipping patches faster too. Your patching processes need to keep up! In this episode we show how to automate patching on a monthly cadence, roll it out in rings, and keep control of the process the whole way through. zero-touch, ring-based patch automation with Tanium deployment plans, in Atlas or the classic console.