Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

From Runtime to Pre-Change Review | Garrett Hamilton x Jonathan Brucato

Much of security work happens at runtime, finding issues after a change has already shipped. Garrett explains how Reach is opening its agents through the MCP server so teams can ask “what if” before a rule or change goes out. The goal is to give the engineers and change control boards reviewing those changes more confidence before they sign off. In the full episode.
Falcon Guardian: CrowdStrike Agent Graph

AI agents don't stop at the answer. They read files, install packages, and run commands on the endpoint, with the user's access. AI security that only watches prompts never sees that part. This demo shows how CrowdStrike Agent Graph in CrowdStrike Falcon Guardian connects AI telemetry with Falcon endpoint telemetry to trace what agents actually do, from prompt to impact. Follow a coding agent from a routine-looking setup note to the tool call that triggered a blocked detection, see the adversary it is linked to, and catch the risky prompt in the same session.

Deploy Kubernetes backup on OpenShift: TrilioVault Manager | Trilio for Kubernetes

Deploy Trilio for Kubernetes on Red Hat OpenShift by creating the TrilioVault Manager, the resource that runs T4K, and open the T4K management console. You will: Best practices covered: change T4K only through the TrilioVault Manager and keep its manifest in version control (the operator reverts changes made anywhere else); size the job deadline from measured backup throughput (the default is 12 hours); measure datamover memory on a representative backup before production; reach the console through the HTTPS ingress, never port-forward.

Install a Kubernetes backup operator on OpenShift | Trilio for Kubernetes

Install the Trilio for Kubernetes backup operator on Red Hat OpenShift from the Software Catalog (OperatorHub on earlier versions), with the settings we recommend for production. You will: Best practices covered: run only GA builds in production and stay on the latest maintenance release of your minor version; approve upgrades through change control; keep T4K alone in trilio-system, because Manual approval applies to every operator in the namespace.

OpenShift backup readiness: CSI snapshots and preflight check | Trilio for Kubernetes

Before you install Kubernetes backup on OpenShift, check that your cluster can take CSI snapshots. This video checks the OpenShift version, StorageClasses and VolumeSnapshotClasses, and runs the Trilio for Kubernetes preflight check. You will: Best practices covered: check the compatibility matrix before every install and every OpenShift upgrade; run the preflight against every StorageClass you protect, and again when you add one; keep CPU, memory and object-count quotas off the T4K namespace.

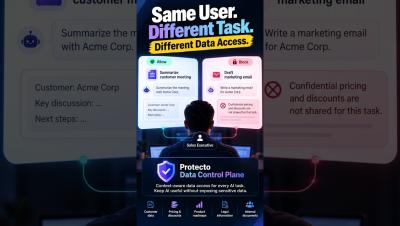
Same user. Same data. Different task. Different access decision. #ai #shorts

A sales executive can view contracts, pricing, discounts, and account details. Ask an AI assistant to summarize a customer meeting, and it needs the customer name. Ask the same assistant to draft a marketing email, and it must not include confidential pricing or discounts. Same user, same data, different task, different answer.

Unified Data Security vs. Multiple Point Solutions: You Need One View of Data

“Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data.” Security teams read headlines like this every week. When they learn about new threats from sources like CISA Cybersecurity Alerts & Advisories, each one prompts a check on whether current tools cover it. And as these new threat vectors get published, some expose gaps that existing tools can’t cover. Teams respond by searching for products to address these risks.

Torq Retrospect: Your SOC's Past Shouldn't Be the Price of Switching

Noam Cohen is Head of Artificial Intelligence at Torq, where he leads the AI research and engineering work that powers the platform’s agentic SOC capabilities. Noam work at Torq spans the core AI systems behind autonomous threat investigation, SOC memory, confidence-based decision thresholds, and the guardrails that make agentic AI trustworthy enough to act in production security environments.

Manage Physical Security with Claude, ChatGPT & Gemini using Brivo's MCP server

What happens when you connect Claude, ChatGPT, or Gemini directly to physical security infrastructure using the Model Context Protocol (MCP)? Traditional portals only answer what they were built to answer - leaving operations and support teams stuck pulling data across a dozen screens. With the launch of Brivo Reseller MCP (the first MCP server for security systems integrators), your AI assistant connects directly to your Brivo partner portal data right alongside your CRM, billing, email, and ticketing tools.

Weak Passwords Can Cost You More Than You Think

Weak or reused passwords can give cybercriminals access to your accounts, often at your expense. As a proud Cybersecurity Awareness Month Champion with the National Cybersecurity Alliance, we're reminding everyone that stronger passwords and smarter security habits make a difference. Don't make it easy for attackers.