Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

PHP2Shell Security Checklist: What to Ask Your Vendors

You might not run PHP yourself. That doesn’t mean you’re safe from PHP2Shell, which is why we created the PHP2Shell Security Checklist. Your SaaS provider might use PHP. Your hosting provider might manage PHP runtimes on your behalf. A third-party application could bundle PHP inside a container or software package you didn’t know existed. This is what makes PHP2Shell a supply-chain security concern.
NIST AI RMF: What It Is and How to Adopt It

One of the jobs of the National Institute of Standards and Technology is to keep on top of new technologies as they are developed and evolve. This is particularly important for risk management, considering both of the major governmental information security frameworks (FedRAMP and CMMC) are based on NIST publications. Well, as you might imagine, Artificial Intelligence technology is a huge new risk factor.

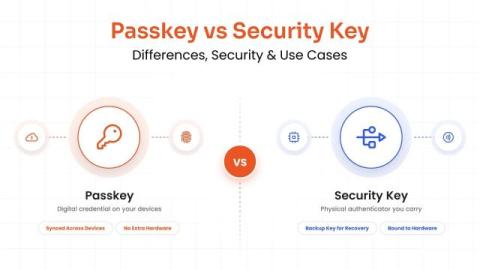
Passkey vs Security Key: Differences, Security & Use Cases

Passkeys and security keys both support phishing-resistant authentication, but they differ in how credentials are stored, managed, and used. A passkey is a digital authentication credential, while a security key is a physical authenticator that can store credentials and prove a user's identity. For enterprises replacing passwords, the distinction affects credential portability, recovery, hardware requirements, and control over authentication.

PHP2Shell: Exposure and Response with the CrowdStrike Falcon Platform

PHP2Shell (CVE-2026-109618 and CVE-2026-109619) introduces two critical remote code execution vulnerabilities affecting PHP, making it important for security teams to identify affected systems, understand their exposure, and investigate potential exploitation.

PHP2Shell vs. Log4j: Understanding the Risk and Exposure | Bitsight Webinar

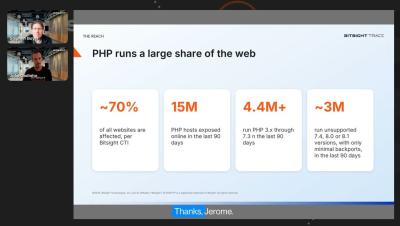
Could PHP2Shell become the next Log4j-scale cybersecurity threat? Newly disclosed critical PHP vulnerabilities are raising concerns about widespread exposure across enterprise environments and third-party supply chains. In this webinar, Bitsight cybersecurity experts examine the potential impact of PHP2Shell, share findings from Bitsight's latest exposure research, and explain how security teams can identify vulnerable assets, assess third-party risk, and prioritize remediation.

Patching at the Speed of Mythos

Can you move faster without risking downtime? Mythos is putting pressure on IT teams to patch in days, not weeks. But September's Patch Tuesday was a reminder that speed comes with its own risk: what happens when the patch you need to deploy quickly is the thing that causes an outage? In this session, we'll unpack what September taught us about faster patch cycles and look at how teams can shorten remediation timelines without giving up the testing and control that keep production running.

Tanium Certified Operator: 2026 Refresh: Tanium Tech Talks #174

The refreshed Tanium Certified Operator (TCO) exam swaps simulations for concept-based Q&A. See what changed, what didn’t, and how to prep. The TCO is the foundational Tanium exam: testing whether you understand the basics of interacting in Tanium. This episode covers what changed in the latest cert refresh, what stayed the same, which version to take, and how to prepare.