Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

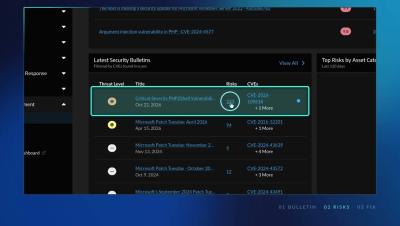
Is My Organization Exposed to PHP2Shell? See It in Aurora Vulnerability Management

PHP2Shell is two unauthenticated remote code execution (RCE) flaws with public exploit code. As AI speeds up the path from vulnerability to exploit, security leaders keep asking two questions. Are we exposed? And what do we fix first? This walkthrough shows how Aurora Vulnerability Management from Arctic Wolf answers both.

PHP2Shell is in CISA KEV: why runtime visibility matters

Five days after PHP shipped the fix, CISA added both PHP2Shell flaws to its Known Exploited Vulnerabilities (KEV) catalog. Federal civilian agencies have until October 29 to remediate. Last week’s question was whether attackers could turn the flaws into working shells. This week’s question is which of your images and hosts still run an affected PHP build, and who can fix each one.

Ep. 91 - PHP2Shell: The PHP Flaws That Can Run a Stranger's Commands Before Your App Even Loads

PHP2Shell is two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, that can let a stranger run commands on your web server without logging in. On Apache mod_php, it can happen before your application code even loads. We unpack which PHP setups are exposed, why PHP says updating is the only safe fix, what to do about end-of-life PHP, and three questions every CISO should ask about a web-tier foothold. Update: on 26 Oct, researchers reported the first successful in-the-wild exploitation.

PHP2Shell Won't Be the Last. Here's Where the Next One Will Show Up First.

On October 17, Amazon's honeypot network logged a PHP2Shell exploitation attempt from an anonymized IP address. Yet, public disclosure was still four days away. By the time PHP got its fixes in on October 21, the technical details had already leaked, proof-of-concept exploits were in wide circulation, and more exploit attempts were being logged left and right.

PHP2Shell Vulnerabilities: What Happened, Who Is Affected and How to Respond

On 21 October 2026, two critical vulnerabilities in PHP, known collectively as PHP2Shell, prompted urgent security warnings from the UK’s National Cyber Security Centre (NCSC) and other cybersecurity authorities. Tracked as CVE-2026-109168 and CVE-2026-109619, both vulnerabilities carry a CVSS v4.0 score of 9.2 and could allow unauthenticated attackers to execute malicious code remotely on vulnerable PHP servers.

Handling PHP2Shell with Tanium Atlas: Tanium Tech Talks #175

PHP2Shell is here. See how Tanium finds PHP across your environment, scopes your exposure, and maps attack paths so you know what to patch first. In this special edition, we walk through how Tanium gives you visibility into the new PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) and the resources available to help you respond.

PHP2Shell Breaks the Internet - The 443 Podcast - Episode 393

This week on the podcast, we dive into a pair of PHP vulnerabilities dubbed PHP2Shell and the chaos they caused through uncoordinated disclosure. After that, we discuss a certificate authority who's random number generator only goes to three digits before ending with law enforcement action around ShinyHunters ransomware negotiators.