Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How cyber incidents become information crises

Customers notice a cyber incident long before investigators finish explaining it. Failed payments and missing services raise questions that demand quick answers. Understanding how cyber incidents become information crises helps organisations respond before confusion damages trust.
How Viddo Holds An Incident Diagram Still While It Moves

Security notes stay readable when the diagram does not grow a second architecture. A customer brief can start from the signed drawing on viddo, then add a short motion pass that leaves every box, arrow, and label on the same page the analyst already approved.
Featured Post

How do you prepare leaders for a security crisis?

Toro Solutions and Insignia Crisis Management recently brought together people experienced in security, crisis management, communications and resilience to discuss how to prepare leaders for a serious security crisis. Most organisations work to prevent serious security incidents and plan how to respond. But a plan can only take you so far. People must make decisions quickly, with incomplete information, while the situation is still changing.

RTO vs RPO: What They Mean and How to Set Them Honestly

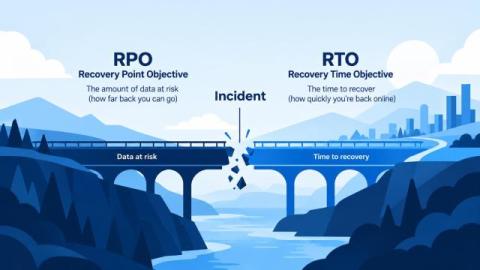
Recovery time objective (RTO) is how long a system can be down before the impact becomes unacceptable. Recovery point objective (RPO) is how much data the business can afford to lose, measured as a window of time before the incident. RTO looks forward from the moment things break. RPO looks backward from it. That distinction takes a paragraph to explain and years to get right, because the difficult part was never the definition.

24 Hours to Paralysis: 87% of Automakers Cannot Survive a Day of Operational Downtime

Two hours of downtime is all it takes to plunge nearly 1 in 5 automakers into an immediate crisis, while 87% cannot sustain an outage beyond 24 hours. With 78.5% of companies running unsegregated IT/OT networks and 5 in 9 of plant managers unprepared for ransomware, a single cyber incident now threatens rapid assembly line paralysis across the supply chain.

4 Easy Steps To Secure Mobile Field Work

A field tech at a customer site can log into a scheduling app, pull up an invoice, and snap a site photo in under five minutes while connected to open Wi-Fi. That mobile device holds customer addresses, signed work orders, access codes, account credentials, and job-site photos. Unlike an office workstation that sits behind a firewall and never leaves the building, a field device moves through unfamiliar networks and high-risk physical spaces daily.

How Clear Communication Strengthens Cyber Incident Response

When a cyber incident hits, your team's technical skills are definitely put to the test. But beyond the digital forensics and system recovery, another skill's just as important for getting through it: communication. Good communication is the backbone of any successful incident response (IR) strategy, but people often don't think about it until it's too late. This guide will show you how to build a clear communication framework for your IR team.

Seeing Thousands of Real Incidents Means I Have No Choice But to Share What I Know

A few years ago, I was sitting across from a security leader at a large enterprise. They had just deployed their first wave of AI agents. When I asked how they were thinking about the security of it, they paused for a moment and then said something I haven’t forgotten. I felt that. Not just as a researcher, but as someone who had been in enough of those rooms to know it was not one person’s gap. It was the whole industry’s gap.

What the Cloudflare Outage Says About Changes Made Under Pressure

Observability is not the problem anymore. The data that tells you a change will break something usually already exists. Most teams have the events, the logs, the configuration history. What is missing is the step that turns all of it into a clear yes or no on a specific change, while there is still time to pull it. Garrett Hamilton, CEO of Reach Security, on objective data and the changes that get made before anyone checks.