Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How UAE Banks Go Live on Stablecoins | Fireblocks x MFTA

Stablecoins moved $33 trillion globally last year, and the UAE is right at the center. Fireblocks' John Hallahan on how banks get from pilot to production. John Hallahan, Head of Business Solutions & Advisory at Fireblocks, joins Raghda Ibraheem to unpack the UAE Stablecoin Payments Playbook from MFTA and Fireblocks, a practical roadmap for banks and payment companies moving from proof of concept to large-scale production.
The 5 Biggest DORA Compliance Mistakes Financial Institutions Make

Are these common DORA compliance mistakes putting your financial organization at risk? The Digital Operational Resilience Act (DORA) requires financial entities to take a structured approach to ICT risk management and digital operational resilience. But organizations can still encounter gaps when translating regulatory requirements into day-to-day controls.

Why Reachability Changes Vulnerability Response

When a critical vulnerability is announced, the first response is often urgency—and sometimes panic. But not every vulnerable asset presents the same level of risk. In this video, Daniel dos Santos, VP of Research, explains how reachability helps security teams move beyond broad vulnerability hunting and focus on the assets that are both vulnerable and exposed in ways that matter to the business. By understanding reachability, organizations can prioritize response efforts, reduce noise, and bring structure to vulnerability management.

Understanding the Impact and Implementation of India's DPDP Act 2023 | Podcast with Adwaita Bhagwat

Privacy is no longer just policy, it’s a legal responsibility. In this Podcast, Vidushi Gupta in discussion with miniOrange Legal officer Adwaita Bhgwat on how India’s DPDP Act 2023 is reshaping data protection, consent, and organizational accountability across every business that handles personal data.

Vanta's The Tabletop: Ep. 2 with Jason Chan

The attacker didn't break in. They logged in. In episode 2 of The Tabletop, Jason Chan (former VP of Security at Netflix) has 26 minutes to investigate an MFA fatigue attack that leads to a forgotten production script with hard-coded credentials... and no owner. His reaction says it all: "Archeology is part of our jobs… figuring out what this thing does.".

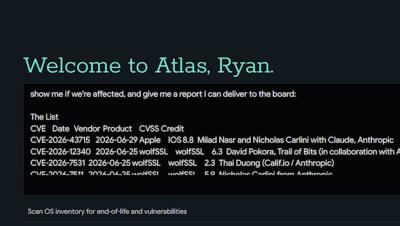
Streamline Exposure Management Responses with Atlas

When 115+ new CVEs are released — Firefox, OpenSSL, WolfSSL, and more — figuring out your exposure used to mean hours of manual work: querying the CMDB, pulling reports, chasing tickets. In this video, we show a faster way with Tanium Atlas. We paste in the full list of CVEs and ask one question: are we affected, and can we get a report ready for the board? In under a minute, Atlas returns a full exposure report across thousands of endpoints, prioritized by what needs attention first. A follow-up question generates a remediation plan. The result.

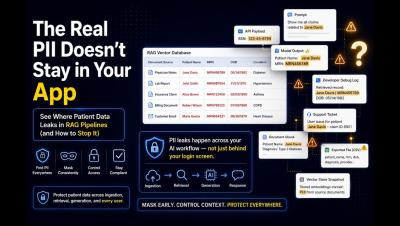
Why Your Healthcare RAG Pipeline Is Leaking PHI (And How to Fix It)

Why Your Healthcare RAG Pipeline Is Leaking PHI Most healthcare organizations believe their AI assistant is secure once they restrict who can log in. Unfortunately, that's only part of the story. Modern healthcare AI applications rely on Retrieval-Augmented Generation (RAG), where patient records, physician notes, insurance claims, and medical documents are embedded into vector databases to power intelligent search.