Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The Importance of Adopting Modern AppSec Practices

Security is an increasingly critical aspect of application development. As the volume of applications rapidly expands, so does the volume of source code, components, and dependencies used to create them. With them comes a growth in the potential attack surface and an escalation in the variety of threats to your application security.

WatchGuard Advanced EPDR Is Now Available in the Unified Security Platform

We are thrilled to announce the launch of WatchGuard Advanced EPDR as part of our Unified Security Platform® architecture. Now available in WatchGuard’s distribution channels, WatchGuard Advanced EPDR is tightly integrated within WatchGuard Cloud and ThreatSync, delivering valuable visibility and intelligence while fortifying cross-product detection and response.

Project Eden: The Technical Perspective

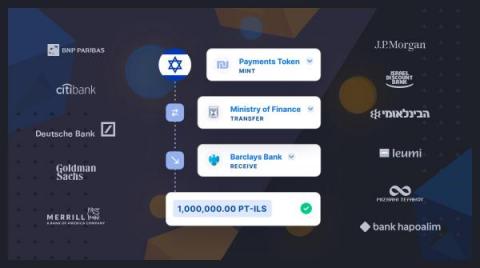
12 of the most prominent banks gathered at Tel Aviv Stock Exchange (TASE) on May 31st, 2023, to participate in Project Eden, a highly-anticipated PoC of the first digital government bond issued by the Israeli Ministry of Finance. International and domestic banks – Barclays, BNP Paribas, Deutsche Bank, Goldman Sachs, J.P.

Checklist for Developers to Build Secure APIs

APIs were already ubiquitous in driving modern applications. However, the pandemic has further accelerated growth in innovation and expansion of digital services, making APIs even more widespread. In today’s world, rapid innovation would not be possible without secure APIs. Attacks on APIs are increasing exponentially. Gartner suggests API abuses are the most significant attack vector since 2022. Hence securing APIs is more critical than ever in the past.

Capturing Secrets from Environment Variables via CircleCI

CircleCI is a platform that enables continuous integration and delivery of software projects. It allows teams to automate their software development process by building, testing, and deploying their code changes in a consistent and reliable manner. In this blog post, we will explore the Tactics/Techniques/Procedures (TTP) of how environment variables that house sensitive credentials and secrets can be exfiltrated using Circle CI.

New Phishing Campaign Uses Hyperlinked Images for Fake Gift Cards and Promotions

A phishing campaign is using hyperlinked images in order to trick users into visiting malicious sites, according to Jeremy Fuchs at Avanan. The emails contain images that offer gift cards or promotions for Delta or Kohls. “Obfuscation is a gift to hackers,” Fuchs says. “It allows them to pull off a magic trick. It works by hiding the true intent of their message. In this case, it’s a picture. The picture is meant to entice the user to click.

Types of Threats Privileged Accounts Face

There are many cybersecurity threats privileged accounts face including phishing, insider threats, malware and brute force attacks. When privileged accounts aren’t managed or secured properly, all of an organization’s sensitive data is vulnerable to being successfully targeted by threat actors. Continue reading to learn how and why cybercriminals target privileged accounts and how organizations can keep their most critical accounts safe.

Movin' Out: Identifying Data Exfiltration in MOVEit Transfer Investigations

CrowdStrike incident responders have been at the forefront of investigating impacted victims of CVE-2023-34362. Since the release of the vulnerability, there has been great collaboration across the cybersecurity industry, and this blog will cover novel details for teams investigating the potential impact to their organizations.