Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

August Release Rollup: Configuration Agent, AI Workflows, and More

The August release brings significant advances across Egnyte, making AI more actionable, connected, and easier to use across everyday workflows. Key updates include the new Configuration Agent, AI-powered agents in workflows, enhanced AI Assistant capabilities, and expanded support for connecting AI tools through Egnyte MCP Server.
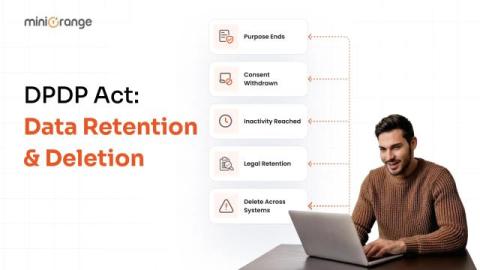
Data Retention Policy Under the DPDP Act: How Long You Can Keep Data and When to Delete It

How long should an organization keep personal data? Under the DPDP Act, the answer is not simply one year, three years, or any other fixed period. The right retention period depends on why the data was collected, whether that purpose still exists, and whether another law requires the organization to keep it.

What Are the Best Plugins for Implementing SSO on WordPress?

Two-factor authentication (2FA) gives your WordPress login an extra verification step beyond the password. If someone gets hold of a password, they still need the second factor to access the account. This makes 2FA particularly useful for administrators, editors, store managers, members, and other users with access to important site functions. The right 2FA plugin depends on your site, user base, and the level of control you need over 2FA.

Cato Managed SASE for SMB: Flexible Capacity, Faster Onboarding

For MSPs and service providers, a managed SASE offering needs to be repeatable across a small and midsize business (SMB) customer base, from selling and licensing, through provisioning and support. But traditional per-customer licensing can introduce friction every time a partner adds or expands a customer. That process can slow onboarding, add administrative work, and limit how partners allocate capacity.

Secure Data Sharing: Best Practices for Privacy and Compliance

Data sharing creates business value only when organizations can control where data goes, who can use it, and what happens after it leaves its original system. That becomes harder as businesses exchange customer records, financial information, healthcare data, and AI-ready datasets across employees, vendors, applications, and regions. The answer is not simply sending files through an encrypted channel.

How 6 Women in Cyber Are Rethinking Risk, Resilience, and Security Leadership

Established by the Canadian nonprofit Women Cybersecurity Society, Women in Cyber Day celebrates the contributions of women across the cybersecurity community and encourages the continued advancement of the profession. Observed annually on September 1, the day also provides an opportunity to spotlight the expertise and perspectives shaping what comes next in cybersecurity, especially as the industry rapidly transforms. Cybersecurity has never had more frameworks, controls, benchmarks, metrics, or tools.

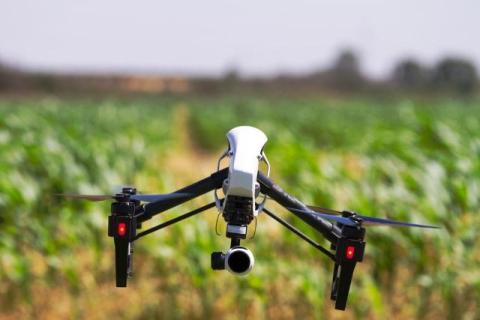
How Drone Data Security Is Becoming Non-Negotiable for Critical Infrastructure Inspections

Infrastructure inspections used to mean a crew with clipboards, a bucket truck, and a lot of guesswork. Now it means a drone circling a substation, capturing LiDAR point clouds, thermal signatures, and centimeter-accurate geospatial data in a single flight, an approach Drone as a Service (DaaS) and similar operators have helped bring into the mainstream. That shift solved a lot of old problems. It also created a new one that most operators haven't fully priced in: what happens to all that data once the drone lands.

Digital Resilience Becomes the Core of Business Stability

Companies now judge their strength not by how quickly they grow, but by how effectively they recover when systems fail. A single outage, ransomware attack, or supply chain disruption can freeze operations for hours or days, draining revenue and eroding customer trust. In 2026, digital resilience shifted from an IT matter to a boardroom priority, guiding how leaders plan budgets and build teams. The goal is no longer to prevent every incident, which is impossible, but to keep essential functions running through turbulence. Firms valuing recovery as strategy outperform reactive rivals.

The Curve Sets Your Attachment, Not Your Limit

The standard method for sizing a cyber program from a loss curve has two halves. Set the retention where the balance sheet can absorb the loss, and set the limit at the one-in-hundred-year figure. The first half is sound. The second is a convention borrowed from property catastrophe practice, and the curve does not derive it. ‍ The distinction matters because organizations treat both numbers as outputs of the same model, then defend a limit the model never produced.