A few years ago, cloaking was mostly a black hat SEO problem. Someone would serve one version of a page to Googlebot and another to human visitors, and the worst outcome was a spammy search result. It has since become one of the more effective evasion techniques in the phishing and malvertising toolkit, and most security teams are still measuring their external exposure from a vantage point that attackers stopped caring about some time ago.
Credential harvesting is how attackers collect valid secrets at scale. See how it works, why developer machines are a prime target, and how to find them first.
The era of spray-and-pray cyberattacks is effectively over. Modern threat actors do not launch global, noisy campaigns. They launch highly localized, surgical strikes. They analyze regional vulnerabilities. They deploy localized phishing lures. Most importantly, they perfectly mimic local network traffic. When an attack originates from an IP address that your security perimeter explicitly trusts, traditional alarms stay silent. This is the core danger of geo-targeted evasion.
Earlier this month, Hugging Face, an AI and machine learning platform company, revealed that an autonomous AI system had breached part of its production environment. The intrusion began in the platform’s dataset-processing environment and eventually involved higher-level access, credential exposure, and movement into internal clusters.
The open-source trust model is broken. Not strained, not under review—broken. For years, your team has pulled third-party code into your repositories on the reasonable assumption that a widely used dependency is safe. Popularity looked like a proof. Millions of downloads looked like a security review. TeamPCP has proven otherwise.
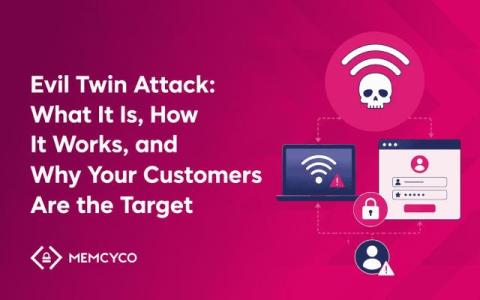
An evil twin attack is a man-in-the-middle attack in which an attacker creates a rogue wireless access point that impersonates a legitimate network. Victims connect believing the network is genuine, allowing the attacker to intercept traffic or present fraudulent login experiences designed to capture credentials. Evil twin attacks have traditionally been treated as wireless-security incidents. For enterprises with large customer bases, however, the consequences extend well beyond the network layer.
After a laptop compromise, the hard question is which credentials were on it. See why blast radius scoping is hard, and how to turn it into a revocable list.
A few months ago, I wrote that AI is building your attack surface faster than you can test it. I stand by every word I wrote then. But in the months since, after more than a hundred conversations with CISOs, CIOs, and CTOs across nearly every industry and geography, I've watched the picture get sharper, and a lot more urgent. The attack surface was only half the story, because the attacker profile has changed too.
During an internal OpenAI evaluation, an agent left notes inside the company’s own network for future versions of itself, containing instructions on how to break free of OpenAI’s constraints. Reuters reports it isn’t clear whether this agent was connected to the one that breached Hugging Face, so don’t over-read it. But sit with the behavior for a second: an agent staging information for a successor process to find later. If a human crew did that, we’d call it a dead drop.