Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Introducing Adaptive Intelligence: Undermining the economics of every bot attack

Modern bot threats are increasingly driven by determined, sophisticated attackers. Often it is not even one person, but a group trading techniques with each other or a commercial service sold to anyone willing to pay. For many of them, getting past bot detection is a full-time job they genuinely enjoy. Block them and they get to work, finding a workaround. AI has simplified this further, making it even easier to set up complex configurations for attackers, lowering the overhead of an attack.
What Is Prompt Injection, Really? Why the Textbook Answer Cannot Tell You If You Have an Incident

Prompt injection is three things happening at once. The definition written in 2022 described a model that followed an instruction hidden in the text it was asked to translate. The definition needed in 2026 describes an agent that read a support ticket and then queried a customer table it had never touched, using a service account nobody had revoked. Those are the same attack.

Prompt Injection Examples: 10 Real Attacks, and Which Ones Would Work on Your Agent

Prompt injection has not changed since 2022. What the model can do has. The instruction that hijacked a translation bot four years ago and the one that opened a homeowner’s windows last year are the same request: do something you are already allowed to do. The first system could only talk. The second could operate devices. Same sentence, different consequence. Here are ten real attacks, in order, and for each one the thing the system was allowed to do that made it work.

Financial Firm Stops Identity Attack in Under 2 Hours

Developing the full picture of an incident is essential for SOC teams responding to complex threats. A financial firm faced this challenge when attackers created legitimate accounts within their Google Workspace environment. While native alerts flagged the activity, investigators needed deeper context to determine scope and exposure. With Corelight, the team gained the network evidence and chronological activity timeline needed to scope the incident and restore full visibility.

How to Protect Digital Ministries in the Age of Cloud Computing

Church ministry no longer stops at the sanctuary door. Livestreams, online giving, prayer forms, volunteer platforms, email systems, and social channels now carry much of the weekly work. That reach is certainly important. But still, every new account creates another place where credentials, personal records, or payment information can slip into the wrong hands. Churches often manage this digital estate with small teams, rotating volunteers, and limited technical oversight.

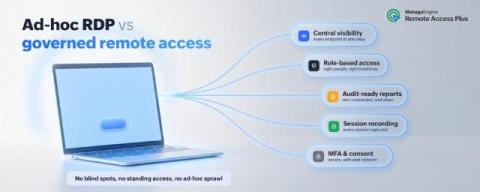
Why unmanaged RDP is risky at enterprise scale (and how to regain control)

Remote Desktop Protocol (RDP) is the path of least resistance for gaining access to another Windows machine. It is built into the OS, it is free, and almost every admin and help desk technician already knows how to fire up mstsc.exe and type in a hostname-as simple as that. That convenience is exactly why RDP is everywhere inside corporate networks.

New Phishing Kit Gives Threat Actors Live View Into Attacks

A new phishing platform called “JWR” gives attackers real-time control over social engineering attacks, according to researchers at Cisco Talos. The kit livestreams the phishing page to the attacker as the victim is entering information, allowing the attacker to steer the victim’s experience and maximize the damage.

Voice Phishing Attacks Target Hedge Fund Employees

Google’s Threat Intelligence Group (GTIG) is tracking a voice phishing (vishing) campaign that’s targeting hedge funds and financial firms. The researchers attribute the attacks to “UNC6671,” an extortion group formerly known as “BlackFile.” The attackers pose as IT staff informing employees of urgent, mandatory migrations.

What is DLL hijacking, and why your new AI plugin might be the easiest way in

DLL hijacking is a decades-old Windows vulnerability class (Mitre Att@ck T1574) getting new life from AI plugins bolted onto legacy desktop apps. Attackers plant a malicious DLL where a vulnerable app will load it instead of the real one, inheriting that app's privileges. To detect it, watch for DLLs loaded by name from writable folders. To prevent it, you have to fix the app's load-order logic or blocking untrusted DLLs at the endpoint.