Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How California Homeowners Can Create a Smarter and Safer Home

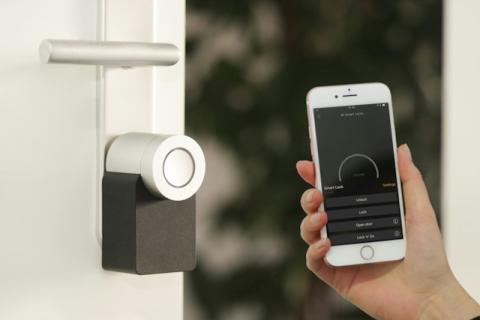
California homeowners face a unique mix of lifestyle considerations, from busy work schedules to varying environmental factors and urban safety concerns. Today's technology enables homeowners to protect their belongings while providing the highest daily level of convenience. Making your home safe is no longer about having a loud alarm; it's about creating a web of interconnected devices that are protecting you and your loved ones proactively.
No Fixed Address: Log4Shell-Style JNDI Injection in Apache Axis 1.x

Apache Axis 1.x is a SOAP engine whose last release came out in 2006. Twenty years later deps.dev counts 384 packages that still depend on 1.4, 83 of them directly, and that single version carries five published advisories. The worst of them turns the client-side service factory into a remote code execution primitive (tracked as CVE-2023-40743, NVD CVSS 9.8, critical).

Salt Claude Connect

Salt Security + Anthropic = a more secure AI ecosystem We’re excited to introduce Salt Claude Connect. This integration will bring continuous MCP server visibility for Claude Enterprise directly into the Salt Security platform. Now you’ll be able to see which organization-managed MCP servers are connected, when they’re added or removed, and their current status (continuously, with no agents, traffic analysis, or manual cataloging required).

CISO Risk Intel Brief: Edge Zero-Days, Identity Residual Risk, and Q4 Control Priorities

This briefing covers two distinct horizons. The past week (23–30 September 2026) is a cluster of material, actively exploited edge and enterprise-application flaws, plus confirmed identity and third-party incidents. The past month (31 August–30 September 2026) shows those events as part of a faster pattern: perimeter appliances as the preferred initial-access class, build systems as ransomware feedstock, non-human identity as a wipe and extortion primitive, and overlapping EU and U.S.

Why Application Security Testing Isn't Disappearing - and How Veracode is Shaping What Comes Next

Application security testing (AST) is the practice of scanning software for vulnerabilities using static, dynamic, and component-level analysis – then managing those flaws through remediation, validation, and certification. A new independent report from FOURCASTERS and Lionfish Tech Advisors confirms that AST is not becoming obsolete. AI and cloud platforms are changing how testing gets delivered, but the need for independent testing, flaw lifecycle management, and validation has only grown.

Microsoft AI Security for SMBs: Purview Coverage Explained

You already pay for Microsoft 365. Before adding AI security, check which tools, accounts and activities your existing controls protect. Then decide what your IT team or managed service provider will manage. Microsoft AI security includes Purview controls for supported third-party AI discovery, sensitive-data protection and prompt-injection detection. Purview may meet your requirements when its licensed and configured controls cover your workflows.

Cloud Management Without Losing Control

Cloud adoption is no longer just a question of where workloads run. Managing a complex cloud environment without a unified view is like running a city with separate control rooms for every utility. While this is quite possible, it likely will be much slower and much harder to manage. In a similar way, the bigger challenge for IT Leaders is maintaining visibility, security, operational control, and evidence for compliance.