Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Lost in Translation: A Native Heap Overflow in Unmaintained Jansi (CVE-2026-8484)

Jansi is the small Java package that makes colored console output work everywhere, including the Windows terminals that never understood ANSI escape codes. You may not have heard of it, but if you build Java, you almost certainly have it on disk: the Apache Maven 3.9.16 distribution puts jansi-2.4.3.jar in its lib/ directory, and Maven's pom.xml declares it as a dependency.

Build the Self-Driving SOC with Tanium Security Operations

Attackers don't wait for humans, and neither should your SOC. Tanium Security Operations brings detection, investigation, hunting, and response together on one platform that moves at machine speed. See how Tanium Atlas works as an extension of your team: pulling live telemetry, historical activity, and the full process tree the moment a threat surfaces, hunting a hypothesis across every endpoint in your fleet, and containing threats from one endpoint to hundreds of thousands. When the hunt needs to go deeper, HuntIQ's hands-on experts take it from there, inside your environment.

Frontier AI Impact Series, Part 1: Why Attackers Stopped Waiting for Zero-Days | Bitsight

Frontier AI can shrink weeks of vulnerability research into exploitation in hours. What does that mean for the flaws your team deprioritized years ago? Bitsight’s Emma Stevens, Senior Threat Intelligence Advisor, breaks it down in the first video of our new series.

Govern the AI agent as the identity it is

AI agents are non-human identities. They hold credentials, carry permissions, and act on systems around the clock, usually with standing access nobody reviews. The Salesloft Drift breach reached more than 700 organizations through exactly that kind of over-scoped, non-expiring token, with no prompt injection involved. The controls already exist: inventory every agent, scope it to least privilege, expire its access, review it on a schedule, and detect when it's abused.

NIST SSDF: 4 core practices for secure software development

The NIST Secure Software Development Framework (SSDF) is a set of fundamental, outcome-based practices that integrate security throughout the software development lifecycle (SDLC). Documented in NIST SP 800-218, it helps organizations reduce vulnerabilities, prevent recurrences, and establish a common language for secure development. The SSDF outlines dozens of tasks grouped into four high-level categories.

A Quiet Shift In Security Every Healthcare Compliance Team Should Read

Change Healthcare took down a third of US claims processing. Ascension spent weeks on the papers. OCR settlements keep citing “risk analysis failure,” and HITRUST r2 assessors are asking harder questions about what actually got tested versus what got scanned. The math on pentesting shifted in the middle of all that. In 2024, 1 in 40 findings was Critical. In 2025, it’s 1 in 10.

How Do I Save My Photos in the Cloud Securely and Privately?

Your phone holds years of memories, and it only takes one lost device, one failed backup or one hacked account to lose them. So if you are asking "how do I save my photos in the cloud?", you are already ahead of most people. The harder question is how to do it securely and privately. Internxt Drive and Photos make uploading and backing up your photos easy, with the added benefits of zero-knowledge encryption, open source software, and data sovereignty.

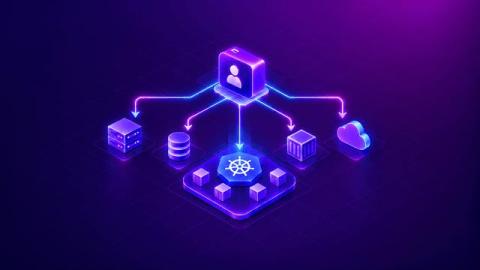
How to Reduce Overprivileged Kubernetes Service Accounts

Overprivileged Kubernetes ServiceAccounts persist when broad RBAC, cloud IAM permissions, and long-lived credentials outlive their intended use. Reduce overprivileged access with least privileged RBAC, scoped cloud permissions, and short-lived certificates that eliminate static credentials. I spent two days last quarter tracking down why a developer could delete production secrets. The RBAC looked fine. The ClusterRoleBinding said edit, not cluster-admin.