Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

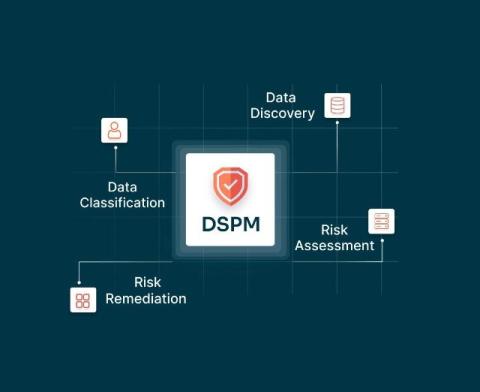
From Metric to Mandate, How CIOs and CISOs Can Operationalize Microsoft Secure Score

This blog is the third part of our series on Microsoft Secure Score. Please read Part 1 and Part 2. As cyber risk escalates in complexity, the role of CIOs and CISOs has evolved far beyond IT governance. Today's security leaders are expected to deliver tangible risk reduction outcomes, maintain regulatory compliance, and support business continuity, often with constrained resources and growing accountability.

Building cybersecurity resilience through governance and assurance

Notis Iliopoulos from Obrela explains why it is time to move beyond checkbox compliance towards true operational resilience and provides advice on how to do it Managing cybersecurity risk exposure and ensuring compliance with evolving regulations has never been more complex or more critical. The rapid expansion of regulatory frameworks such as NIS2, DORA, and GDPR, to name a few, has forced organisations to rethink their approach to governance, risk and compliance (GRC).

DeepSight by Protecto: AI-Native Sensitive Data Detection for Developers

Thanks to a wide range of use cases that automate manual activities, enterprises are rushing to integrate GenAI into their IT stack, only to realize they’ve hit a privacy wall. A concerning number of use cases involve the use of sensitive data like PII and PHI, risking data privacy and compliance. Enterprises today are becoming increasingly aware of these multifaceted risks associated with unfiltered AI usage and turning to the common solution available in the market – AI privacy tools.

Random but Memorable - Episode 15.0: 150th Episode Special

Random but Memorable turns 150! (It’s official, we’re old.) To celebrate, we play some special messages submitted by you – our listeners and customers – along with our own 1Password employees. We’re even sharing some crowdsourced 1Password tips for good measure. We also host a very special Archive Edition of Watchtower Weekly. We look back at some of the historic news stories we covered in 2018 and reflect on how the world of cybersecurity has changed.

How Professional Photography Has Changed Over the Last Decade

Over the past decade, professional photography has undergone a significant transformation, driven by technological advancements and evolving client expectations. The shift from traditional DSLRs to mirrorless cameras has provided photographers with lighter, more versatile tools, enhancing mobility and efficiency on shoots. Simultaneously, the rise of computational photography, particularly in smartphones, has empowered amateurs to capture high-quality images, increasing competition in the industry.

The Rise of Industry-Specific Cyber Defenses

You've probably noticed that digital security no longer feels like a background process. It's front and centre in boardrooms, startup pitches, and industry expos. But here's what's quietly shifting beneath the headlines: cybersecurity is splintering. What used to be a generic layer of protection is now becoming something deeply tied to a business's core operations. Hospitals aren't just worrying about hackers-they're defending against threats that target how medical records are shared.