Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Top 9 Log Analysis Tools

Logs tell the hidden story of your IT infrastructure – what’s working, what’s breaking, and what could be under attack. You’re left sifting through a chaotic stream of events, risking missed insights crucial for maintaining security and operational stability. And the stakes couldn’t be higher. The average global data breach cost hit $4.45 million, with U.S. companies facing an even steeper $9.48 million per incident.
What is MITRE D3FEND?

Being a security analyst today is hard. You’re constantly trying to protect your organization while feeling like attackers are always a step ahead of you. Every year, you seem to add more security technologies to your stack, yet you still find yourself facing tooling gaps. If only you had the ability to clearly compare different products and their capabilities, you think.

Breaking the Mold: Why Differentiation Matters in the SIEM Market

As I celebrate my first year as head of product management at Graylog, I’ve had the unique privilege of re-immersing myself in the world of Security Information and Event Management (SIEM) from a new perspective. The past year has underscored one critical lesson: staying competitive in SIEM isn’t about adding features; it’s about finding fresh approaches to meet the real needs of security teams.

Federated Analytics: Analyze Data Wherever It Resides for Rapid and Holistic Security Visibility

Data is everywhere, sprawling across cloud, on-premises, and hybrid environments. As security practitioners, we need fast access to this data to analyze it, draw insights, and uncover potential threats. However, the sheer volume of data and complexity of threats makes it difficult to maintain visibility, detect stealthy attacks, and respond quickly to security incidents.

Best Practices for Writing an IT Security Incident Report

Everyone remembers that one required writing class they needed to take. If you’re like a lot of other security analysts, you assumed that your job would focus on using technology, not writing research papers. However, in today’s business environment, cyber incidents are critical business events, especially as governments and agencies create more reporting requirements.

Unify and Automate TDIR Workflows with Splunk SOAR 6.3 and Splunk Enterprise Security 8.0

Security teams are juggling 25+ different security tools that perform different actions across detection, investigation and response. Look up an IP here, send malware to a sandbox there, block an executable over there. What’s worse is that the vast majority of those actions are being performed manually. This approach is simply too slow against fast-moving attackers and malware, and it certainly isn’t sustainable.

The Digital Operational Resilience Act (DORA) is coming - are you ready?

As the official implementation date approaches for the Digital Operational Resilience Act (DORA) – financial institutions and their information and communication technology (ICT) service providers, across the European Union are gearing up for a significant shift in their operational landscape.

SOAR in Seconds - Playbook Building with Natively Integrated SIEM and SOAR

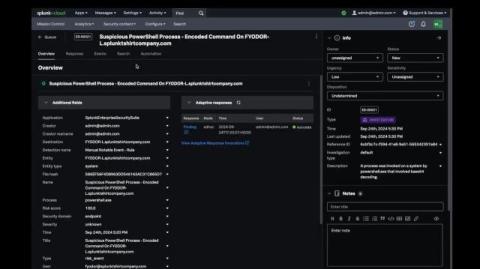
In Splunk SOAR 6.3, SOAR features now come fully integrated with Splunk Enterprise Security 8.0. In this demo, see how to easily create a Splunk SOAR playbook in the context of your SIEM workflows. Playbooks and actions are now directly integrated within the Splunk Enterprise Security analyst queue. You can run playbooks and see the results without leaving the Splunk Enterprise Security interface. Both a Splunk SOAR and Splunk Enterprise Security license is required.

Announcing the General Availability of Splunk Enterprise Security 8.0

At.conf24 we unveiled the private preview of Splunk Enterprise Security 8.0, and the buzz was undeniable. Today, we are thrilled to announce that Splunk Enterprise Security 8.0 is now generally available! This isn’t just another release—it’s a massive leap forward that redefines and revolutionizes security operations. Splunk Enterprise Security 8.0 is the cornerstone of the SOC of the Future.