Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

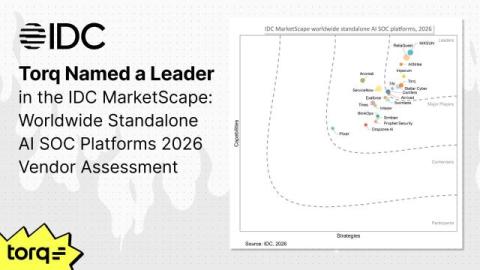
Torq Named a Leader in IDC MarketScape: Worldwide Standalone AI SOC Platforms 2026 Vendor Assessment

Chris Kissel, Vice President of IDC Security & Trust, just drew a line in the sand for the AI SOC category with one simple sentence: “Vendors that can show their agents reason transparently, act within defined guardrails, and improve with each investigation will define this category. The rest will be measured against them.” We couldn’t agree more.
Building Mobile Apps That Scale: A Business Leader's Perspective

Most mobile apps are built for the business as it exists on launch day. The trouble starts when the business keeps growing. A customer app that worked well for 5,000 users begins to slow down at 50,000. An ordering app that served one region struggles when the company expands nationwide. New features take months instead of weeks, and every release feels risky. These are not signs of bad luck. They are signs of an application that was never designed to grow.

AI guardrails aren't security controls

AI guardrails are sold as a solution to keep models behaving as intended - but it can be hard to figure out what you’re getting. The problem starts with the word itself. "Guardrails" means different things depending on who's selling them. Some vendors use it for simple prompt filtering, others bundle in entirely different controls and call it "guardrails" because the word sounds reassuring. Without a shared definition, buyers can't easily tell what they're actually getting.

The Autonomous SOC Was a Promise SOAR Never Kept

David Melamed is Head of Emerging Technologies at Torq. He joined through Torq’s acquisition of Jit, which he co-founded and has led as CTO since 2020, building agentic security on a production Context Graph. A cloud security veteran with 20+ years of experience, David previously held senior technical roles at Cisco (via the CloudLock acquisition) and MyHeritage. For all the gods and monsters in The Odyssey, the ship mostly moves for one reason: men row it.

On-call during local work hours: a PagerDuty rotation manager built in Tines 3B

Global teams run into the same problem with on-call: a single rotation means engineers outside the primary time zone get paged outside their working hours. This walkthrough shows an internal app built in Tines 3B that manages a daytime on-call roster and syncs it to PagerDuty.

Shadow IT Was Just the Beginning. Meet Shadow Automation.

Most security leaders remember the first time they discovered shadow IT inside their own organization. A business team had adopted a SaaS application, connected it to company data, and built a workflow around it before anyone in security knew it existed. The tool was useful, and the team was productive. The governance conversation simply started months late. The agentic enterprise is creating a more consequential version of that problem.

How Low-Latency Infrastructure Supports Automated Trading

Automated trading sounds simple on paper. You write a set of rules, a program follows them, and trades happen without you watching the screen. In practice, the speed and reliability of the system behind those rules matter just as much as the rules themselves. This is why many traders look at tools like a trading VPS, which is a virtual private server that runs your trading software in a professional data center instead of on a home computer. To see why that matters, it helps to understand what low latency really means and how it shapes every automated trade.

Three AI SOC Differentiators That Separate Real From Marketing

Every vendor in this category now says the same word: agentic. I understand why. It’s what the market wants to hear. But when you’re the one signing the contract, “agentic” tells you almost nothing. I’ve sat on the buying side of enough of these conversations to know that the label and the capability are often two very different things.

Buying an AI SOC Isn't Like Anything You've Bought Before

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to Virgin Atlantic, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.