Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

From CVE Disclosure to Internet-Wide Exposure: How Bitsight Uses AI to Accelerate Product Fingerprinting

When a new CVE drops, getting notified is the easy part. The real challenge comes right after. Depending on how your organization is set up, different teams have to scramble to figure out if you're actually using the affected product, which specific versions are exposed, whether it's lurking anywhere in your subsidiaries or vendor ecosystem, and how urgently you need to patch it.
Best Dark Web Monitoring Services for Business

Most security stacks still find out about stolen credentials the hard way: when an attacker logs in with them. Sometimes the first warning sign is a customer complaint or a call from law enforcement. Dark web monitoring services for business close that gap by watching underground sources for any exposure tied to your domains, employees, code, and brand, so you can reset access before someone else gets there first.

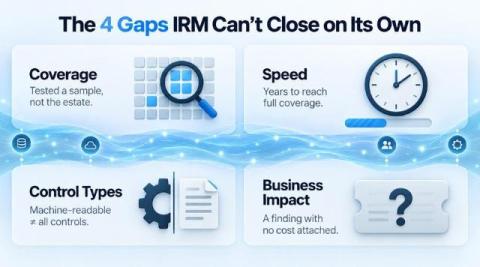
Four gaps IRM was never built to close

A buyer’s checklist for the IRM gaps a ServiceNow program leaves open. Many teams deploy IRM, watch the assessments come back clean quarter after quarter, and reasonably conclude they are covered. Months later, the greatest risk turns out to have been outside the sample. It may have changed the week after the review, or lived in a control type nobody tested, or lacked context or prioritization to see its importance.

When One AI Model Fails Many Companies at Once

Cyber insurance works because losses across a book are mostly independent. One insured suffering ransomware tells you little about the next, so a portfolio of many policies is more predictable than any single one. ‍ Shared AI dependencies break that assumption in a specific way. Where a large share of a book depends on the same foundation model or the same inference infrastructure, a single failure produces simultaneous claims across insureds with no commercial relationship to each other.

Never Join AI Telemetry on Byte Counts

A browser sensor reports that somebody pasted 18,000 characters into an AI tool. A network sensor reports a 24 kilobyte upload to the same destination. Joining those two records on size looks reasonable and is the wrong instinct. ‍ The two numbers describe different objects with several transformations between them, and the transformations do not all run in the same direction. The error cannot even be signed, which rules out a tolerance as well as an equality. ‍

How to Evaluate and Choose the Best Risk Management Software in 2026

Evaluating risk management software in 2026? Here is the moment it has to survive. A board member or an auditor asks what your risk posture is today, not last quarter. You either have it ready to show, or you are rebuilding a register that went stale weeks ago. This video follows one risk through its entire life inside a platform, and uses that path to lay out five criteria for judging any tool, plus the question to put to each vendor.

Digital Risk Protection in the Age of AI

Digital risk has expanded far beyond the traditional security perimeter. Brands now operate across social platforms, advertising ecosystems, messaging applications, collaboration tools, marketplaces, and dozens of other digital channels. Each represents an opportunity to connect with customers. Each also creates opportunities for abuse. A fraudulent advertisement can direct users to a spoofed login page. A fake social media account can support an executive impersonation campaign.

Cloud Risk Management for MSPs: From Visibility to Control

Guest post by Neil Holme, Founder and CEO of Impact Business Technology, a WatchGuard partner. The cloud environments MSPs manage change every week. Clients adopt new SaaS applications, AI tools, and collaboration services, making it difficult to track what is in use, how it is configured, and which access permissions remain active. Exposure grows without a clear warning sign until an incident occurs. The cloud is also the fastest-growing attack surface an MSP manages.

How AI Changes Exposure Management: From Static Findings to Continuous Risk Decisions

Every security team knows the feeling. The quarterly vulnerability scan completes. The report lands, with thousands of findings, color-coded by CVSS severity, neatly timestamped. And the moment it’s printed, it’s already out of date. That is the fundamental flaw at the heart of traditional exposure management: it is built around a point in time.