Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

UNC Path Hardening Quick Knowledge Guide

UNC paths allow Windows systems to access shared network resources, but they can also be a target for cyberattacks if not properly secured. In this video, we break down the Hardened UNC Path policy—a crucial security feature that enforces mutual authentication and integrity checks on critical shares like NETLOGON and SYSVOL. You'll learn: How the Hardened UNC Path policy works Step-by-step setup using Group Policy and registry keys How SMB encryption can add extra security (and its compatibility risks)
10 Insider Threat Indicators & How to Prevent Them

Insider threats are rising, and most organizations aren’t ready to stop them. 76% of companies have seen an increase in insider threats over the past five years, but fewer than 30% feel equipped to handle them. These threats don’t trigger alarms like external attacks—they unfold quietly, often going undetected until it’s too late.

When Security Fails: Be READY | Former Federal CIO Warning

"Something's going to happen." Maria Roat, former Deputy Federal CIO, delivers a wake-up call about the inevitable nature of security incidents. In this crucial clip from Data Security Decoded, Maria reveals why response preparation is everything and how to minimize damage when (not if) breaches occur. Don't wait until "all your data went out the door" - learn proactive strategies from a federal tech leader who's seen it all!

Meeting Compliance Requirements with the Cato LAN NGFW

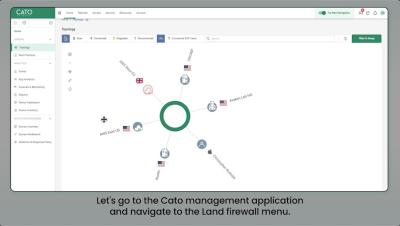
Simplify Compliance & Security with Cato’s Application-Aware LAN Firewall! In a distributed, cloud-first world, ensuring networking and security compliance is more challenging than ever. VLANs lack the granularity needed to enforce strict regulatory controls, and traditional firewall appliances add cost, complexity, and management overhead. What if you could extend your FWaaS to enforce microsegmentation inside the LAN?