Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What's new in Tines: July 2026 edition

July was an exciting month in the world of Tines. We launched Tines 3B, the single, secure environment for every team’s apps, agents, and automation. It’s a new platform where everyone can build, while you safely run and monitor your organization’s most important work. The Tines platform you already know is now called Tines Stories, and we’ll continue to invest in, support, and develop it.
WhatsApp Usernames: Privacy Feature Brings New Impersonation Risks

WhatsApp has begun rolling out usernames, letting people connect without sharing their phone number. The feature adds privacy for individual users but opens fresh territory for impersonation, lookalike accounts, and smishing, particularly as usernames are reserved on a country-by-country basis.

How to Write a POA&M That FedRAMP Reviewers Accept

FedRAMP moved POA&Ms to agencies and replaced them with Accepted Weaknesses under the 2026 rules. Cloud providers must evaluate vulnerabilities in context (criticality, reachability, exploitability, detectability, prevalence, privilege, proximity, known threats), report results in JSON with PAIN N1–N5 ratings, and assume attacker automation. Remediate high PAIN, internet reachable risks fast; low PAIN risks can be accepted. Machine-readable data and platforms can help meet requirements.

AI Security Policy in Practice: How to Define What AI Can and Cannot Do

Most organizations that try to write an AI security policy start with two lists. Approved tools and banned tools. But, that list is inevitably out of date within a month. Employees adopt AI features embedded in everyday software faster than any review board can evaluate them, and a blanket ban does not stop the behavior, instead it pushes people toward personal accounts and unmanaged services.

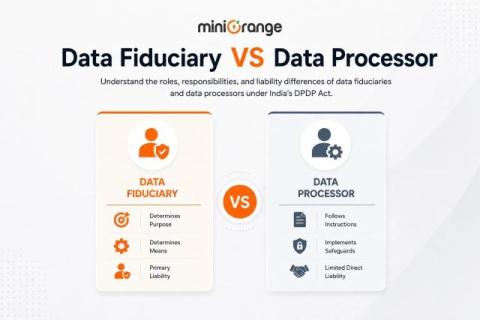
Data Fiduciary vs Data Processor: The Key Distinctions Under the DPDP Act

Under India's Digital Personal Data Protection (DPDP) Act, 2023, every organization that handles personal data falls into one of two roles: data fiduciary or data processor. A data fiduciary decides why and how personal data is processed. A data processor carries out those instructions on the fiduciary's behalf, with no independent decision-making authority. The distinction matters because the DPDP Act ties accountability, liability, and contractual duty directly to which role you occupy.

How does EDR work? Architecture, monitoring, detection and response explained

EDR (endpoint detection and response) works by deploying sensors on protected endpoints to continuously collect selected behavioral telemetry, forwarding that telemetry to a centralized analytics layer, commonly cloud-hosted, that applies detection rules, behavioral analytics, machine learning and threat intelligence, and surfacing prioritized incidents in a console where analysts can investigate and respond.

Scale Your Engineering Organization Without Losing Control

Growing engineering organizations all hit the same wall. More teams shipping software means more repositories, more permission requests, more onboarding cycles, and eventually one platform admin fielding every change. The platform that was supposed to accelerate delivery has now become the bottleneck. JFrog Projects is built to break that pattern.

Warning: Compromised Hotel Routers Send Users to Phishing Sites

Attackers are using compromised hotel Wi-Fi routers to redirect users to Microsoft 365 phishing sites, according to researchers at ReliaQuest. The attacks were observed in multiple U.S. cities, as well as across India and Saudi Arabia. These types of DNS poisoning attacks can send users to phishing sites with very little evidence that something suspicious has taken place.