Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Enforce custom rules in Datadog IaC Security scanning

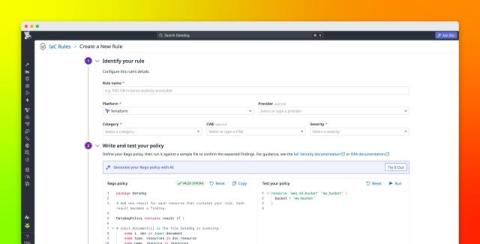
Infrastructure-as-code (IaC) security scanning can catch common misconfigurations before deployment, but every organization also has internal requirements that a default rule catalog cannot cover. For example, teams may need to enforce required tags, approved instance types, or naming conventions. With custom rules for Datadog IaC Security, security and platform teams can define these requirements as Rego policies and run them alongside Datadog’s default rules during IaC scans.
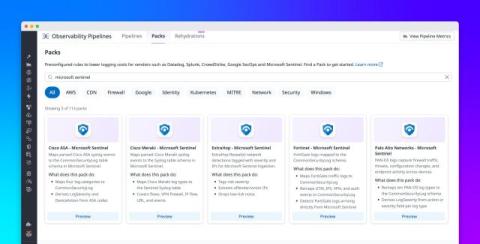
Transform and route security logs to Microsoft Sentinel tables using Observability Pipelines

Microsoft Sentinel is Microsoft’s cloud-native SIEM for detecting, investigating, and responding to threats across your environment. To query security data and run analytics rules, Sentinel expects telemetry data in specific table schemas. But firewall, VPN, and network detection logs arrive in vendor-specific formats, making source-specific mappings difficult to maintain as environments grow.

Stop runtime threats with Workload Protection response actions

Modern threats increasingly unfold at runtime, where attackers exploit live workloads, spawn malicious processes, and move laterally across your environment. Detecting that activity is essential, but a signal only matters if you can stop it. When a threat appears, every step before a response gives an attacker more time to act. Datadog Workload Protection can now directly remediate threats with both automated and manual response.

Respond to security threats faster with Tines and Observability Pipelines

Security teams face a flood of noisy logs that arrive in many formats, and often without the context teams need to detect and prioritize threats. But even normalized and contextually enriched log data is only as useful as the speed at which teams can act on it. Any step that requires manual effort can become a bottleneck that makes it difficult to keep pace with the volume.

Reduce sensitive data exposure with build-time allowlists

Build-time allowlists help teams preserve readable Real User Monitoring (RUM) action names while reducing the risk of exposing runtime-generated sensitive data. RUM action names turn user interactions into descriptions that engineers can use to understand application behavior, but that readability can also create risk. Datadog provides a build-time privacy approach that preserves readable action names when their contents are known to be static while masking text constructed at runtime.

What we learned about AI agent security by monitoring our agents

AI agents comprise models, instructions, data, and tools, so thoroughly investigating potential security risks requires evidence from several components. As Datadog teams build AI agents for internal workflows, we use Datadog AI Guard to monitor how they handle each component during a session. We’ve found that application logs may capture an agent’s final API call without showing which prompt, retrieved content, or tool result led to the action.

From signals to systemic risk: Building Risk AI

Security and engineering teams contend with a constant stream of signals about vulnerabilities, incidents, misconfigurations, identity risks, control gaps, and other findings across their environments. But an individual finding’s severity does not always reflect its potential organizational impact.

Detect vulnerabilities in LLM applications with Datadog's AI-native SAST

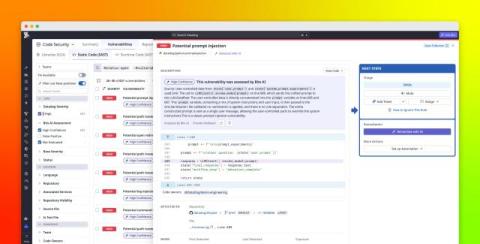
AI coding tools help developers build and deploy LLM applications quickly, but this speed comes with new security risks. Traditional static application security testing (SAST) tools that are pattern based weren’t designed to detect LLM-specific issues such as prompt injection sinks and exposed system prompts. These vulnerabilities often don’t become apparent until applications are already running in production, when remediation is more difficult and expensive.

How CISA's BOD 26-04 changes vulnerability prioritization

AI-accelerated attacks are redefining the threat landscape, but many of them still rely on one of the oldest tactics in the book: exploiting known vulnerabilities. The difference today is speed. Vulnerabilities that once took skilled hackers months or weeks to exploit can now be weaponized in hours or minutes. This acceleration is forcing organizations to rethink how they identify and remediate risk.

Avoid Azure secret rotation with secretless authentication

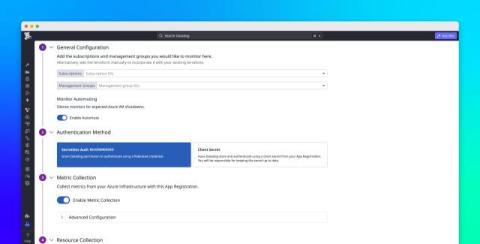
Many observability platforms authenticate to Microsoft Azure by using client secrets. Teams must create, store, and periodically rotate these secrets to keep receiving the telemetry data that they need. This recurring maintenance adds operational overhead and increases the risk of ingestion outages that occur when secrets expire.