Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

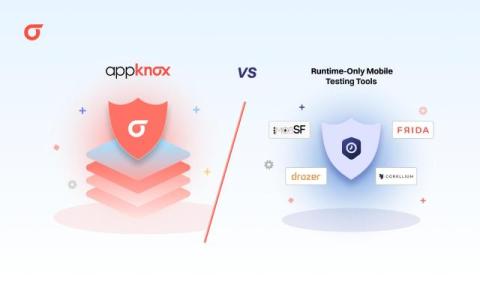
Appknox vs Runtime-Only Mobile Testing Tools: What Dynamic Analysis Cannot See Before the App Runs

Frida hooks into your app's running process in seconds. It intercepts API calls, dumps the keychain, bypasses SSL pinning, and reveals exactly what the app does at runtime. Frida is also the tool attackers use to do the same things to your users. Runtime testing tells you what happens when an app runs under test conditions. It does not tell you whether the app can resist those same tools when an attacker uses them in production. That answer is not in the runtime session. It is in the binary.
From Data to Decision: How Trusted Threat Intelligence Cuts Through the Noise

Security teams are not short of data; they are short of intelligence they can trust. This piece explains how raw threat data becomes trusted, actionable intelligence through validation, attribution, and enrichment, and why the distinction matters as false positives and threat volumes continue to rise.

Data Growth Tests Backup Capabilities: How to Keep Up

Quick answer: Data is growing faster than most organizations can store or protect it. Falling hardware costs, abundant bandwidth, paperless workflows, and regulatory mandates all fuel this surge. To keep critical data safe and recoverable, many organizations now outsource backup to specialists like 11:11 Systems, which delivers secure, compliant, cost-effective cloud backup. Picture a closet you keep stuffing with all kinds of clutter.

mTLS for AI Agents

AI agents are increasingly accessing APIs, databases, SaaS applications, MCP servers, and other services without human intervention. As these autonomous systems become part of enterprise infrastructure, organizations need reliable ways to verify their identity before granting access to sensitive resources. Traditional authentication methods such as API keys and bearer tokens were designed for applications and users, not autonomous agents operating continuously across distributed environments.

A Guide to ISO 27001 Clauses - Updated for 2026

Around the world, nearly 100,000 businesses have navigated the challenges of ISO 27001 and earned their certifications. If you want your business to be the next on the list, you need to understand the 11 clauses that make up the security framework, including what they are, why they exist, and what they require you to do. Let's start where you might reasonably expect to begin: with a definition of what the clauses are.

Securing Commercial Properties After Severe Storm Damage

When a severe storm hits a commercial facility, the aftermath can be catastrophic. High winds, torrential rain, and flying debris disrupt daily operations and threaten structural stability. Property managers face immediate pressure to protect the assets and minimize financial losses. Taking immediate control of the situation prevents minor issues from turning into major disasters. Speed matters when dealing with natural elements that continue to damage a building long after the clouds clear. A proactive response limits operational downtime.

Dedicated Server Hosting: Benefits, Use Cases and Pricing in 2026

Despite the rapid growth of cloud platforms, the dedicated server market continues to expand. Many companies still choose dedicated server hosting for hosting corporate applications, databases, SaaS platforms, high-traffic web services, and artificial intelligence infrastructure. The reason is simple. Not every workload can be efficiently handled in a virtualized environment. Many projects require guaranteed computing resources, consistent performance, full server control, and the ability to customize hardware according to specific business requirements.

A day in the life of a SOC analyst-and what actually slows them down

In the current threat landscape, the pressure on security operations center (SOC) teams has never been higher. Yet for many organizations, the reality of daily security operations is less high-tech threat hunting and more of an uphill battle against manual processes and fragmented data. To understand why SOC teams are burning out, let's walk through a typical morning of an SOC analyst.

What Is an RFP Response? A Guide for Security and GRC Teams

A request for proposal (RFP) response is a vendor's formal reply to a procurement document where a prospective buyer outlines all the information they need to make a final purchasing decision. It acts as a detailed pitch, typically covering pricing, solution architecture, references, and implementation timelines. For security and governance, risk, and compliance (GRC) teams, the section that consistently creates the most friction is the security and compliance questionnaire embedded inside an RFP.