Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Evaluating Risk Remediation Software for Enterprise Scalability

Enterprise software delivery is accelerating with more applications, more teams, more pipelines, more third-party code shipping faster than ever. And you can add the compounding risks of AI onto all of that. At the same time, compliance pressure is rising across development, security, and audit teams.
Magento Zero-Day: Unpatched Adobe Commerce RCE Is Backdooring Online Stores

On 4 September 2026, attackers began exploiting an unpatched remote code execution flaw in Magento Open Source and Adobe Commerce. Dutch e-commerce security firm Sansec disclosed the issue on 5 September and named it StyleSmuggler. The company said it published early because stores were being compromised in real time.

What's new in Tines: August 2026 edition

More teams are building Apps in Tines Stories to deliver their most important work. This month, you can connect Apps to your Tines data, assign clear ownership, and share view access through your identity provider. Bring your data directly into an app. Apps can now read cases, records, and resources through built-in Workbench functions, so you spend less time configuring Workbench tools and building endpoints to interact with your data..

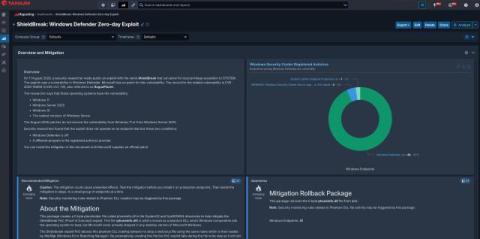
Hunt or be Hunted: ShieldBreak Zero-Day

On August 11, 2026, a security researcher publicly released a proof-of-concept called ShieldBreak, a full bypass of Microsoft’s own July patch (RoguePlanet) for a Windows Defender privilege-escalation flaw, with a reported 100% success rate against Windows 11 25H2 and Windows Server 2025. No vendor fix existed for the bypass. The only real defense was whoever moved first.

How to prevent chaos in the Microsoft AD estate: A quick-start guide to reduce risk and administrative burden in medium-sized regulated businesses

If you work in IT for a medium-sized regulated business, you already know the truth: Your Microsoft environment didn’t become sprawling overnight. It grew through mergers, acquisitions, divestitures, reorganizations and the natural evolution of a business that’s constantly adapting. Every new business unit brought its own domain. Every acquisition added another tenant. Every project introduced new accounts, groups and privileges.

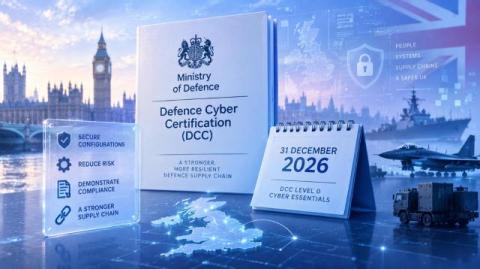
December 2026 Is Closer Than You Think: What the UK's Defence Cyber Directive Means for Your Organisation

The UK’s Ministry of Defence has sent a clear message to organisations within the Defence supply chain. By 31 December 2026, all Defence industry partners are expected to achieve Defence Cyber Certification (DCC) Level 0, including Cyber Essentials for all applicable business-critical systems within scope. This represents a significant step in strengthening cyber resilience across the Defence ecosystem and raising the baseline for cyber security throughout the UK’s supply chain.

Adopting & Implementing Zero Trust: Moving from Concept to Execution

Zero Trust is often summarized as “never trust, always verify.” More precisely, it is a security model built on the premise that trust should never be granted implicitly based on where a user, device, workload, or resource sits. That makes Zero Trust much bigger than deploying a particular product or turning on a handful of access policies.

Why Network Privacy is Becoming a Critical Layer of Modern Cybersecurity

In 2026, network privacy has become a critical layer of modern cybersecurity. With cyber threats becoming increasingly advanced and businesses embracing hybrid work, cloud platforms, and interconnected systems, network security can protect data moving across networks and reduce exposure to cybercrime. This article will explore why network security is so important in 2026, the risks associated with unsecured connections, and how businesses can strengthen their posture. Read on to find out more.