Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What is cyber due diligence?

Due diligence in a merger or acquisition is, by design, exhaustive. It brings a level of scrutiny that touches almost every part of a business. From financial audits and legal reviews to commercial assessments, buyers work hard to make sure nothing important gets missed. And yet there’s one area that continues to catch organisations off guard, even in the most professionally run due diligence processes: The cost of a data breach has never been higher. Digital estates have never been more complex.
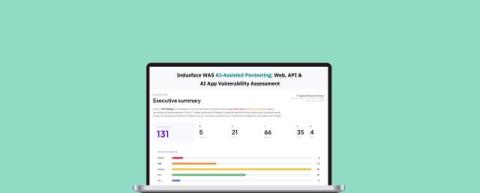

Indusface WAS AI-Assisted Pentest: Comprehensive Vulnerability Assessment Across Web, API and AI Apps

For years, our security team has run pentests against business-critical applications across industries, and one pattern stands out. The vulnerabilities that are the most difficult to remediate are business logic vulnerabilities: IDOR, broken access control, privilege escalation, and multi-step workflow abuse. These are the kind of vulnerabilities pentest experts find by noticing a broken assumption behind one API call and chasing it until the full exploit path becomes clear.

Quantifying Cyber Risk Without Revenue to Lose

A public body has no revenue to lose, no share price to move and no insurance market pricing it the way one prices a manufacturer. It faces the same regulatory pressure to quantify cyber exposure as anyone else, and the standard model's central input does not exist. ‍ Substituting the loss categories is the easy half and it is where most guidance stops. The harder question is what the resulting figure is for, because the decisions a private company makes with it are mostly unavailable. ‍

When the AI Arrives Inside Software You Already Bought

An application that was AI-free at the last audit may be processing corporate data through a language model today. Nobody procured it, nobody approved it and nobody was asked. A vendor shipped a release. ‍ Third-party AI governance is built almost entirely around procurement. Assess the vendor, negotiate terms, sign a data processing agreement, add the tool to a register. The apparatus requires a purchasing event, and an embedded feature produces none, so the apparatus never engages. ‍

What Is MFA for Air-Gapped Networks? Closing the Last Security Gap in Isolated Systems

Air-gapped networks are supposed to be untouchable. No internet connection, no remote pathway, no way in for an attacker sitting halfway across the world. But ask any security team that has actually run one of these environments, and you'll hear a different story. Air gaps stop remote attacks cold. But they do almost nothing to stop a stolen password, a careless USB stick, or an insider with too much trust and too little oversight. That's the gap, and Multi-Factor Authentication (MFA) is here to fill it.

Key Features of an Insider Risk Management Program

Most organizations already have an insider risk management (IRM) program in some form. They have a tool, a dashboard, and an analyst reviewing alerts. What they often lack is a program built on the specific capabilities that turn activity logs into stopped incidents and reduced insider risk.

We gave all our employees access to Tines 3B. Here's what happened next.

In July, we launched Tines 3B to the world, and it’s been incredible to see the response from our customers. It wasn’t a surprise though, we had a sneak peek of how much value 3B could bring when we launched it internally. On June 2, around eight weeks before the product's general availability, we unlocked the doors of 3B, let every single Tines employee into our own instance, and invited them to start building.

Top 4 enterprise risk management software solutions

Good enterprise risk management software gives you one place to record and score every risk, keeps that record current by watching your controls instead of waiting for a quarterly review, maps risks to the frameworks you report against, connects to the tools your teams already use, and turns all of it into dashboards your executives and board will read. The hard part is telling which products do those things well and which just store risks in a nicer grid. Below are the features that matter, a scorecard to weigh them, and four tools worth a look.

Why Sales Commission Data Needs the Same Audit Trail as Any Other Financial Record

An unexpected data integrity question has crept into sales operations: can a company actually reconstruct how a commission payout was calculated months after the fact? For teams still running compensation through spreadsheets, the honest answer is usually no, and that blind spot carries real financial and compliance weight.

How AI Phone Calling Is Changing Voice Phishing Defense

Phone scams have been around for decades, but the last few years have brought a sharp shift in how convincing they've become. Voice phishing, often called vishing, used to rely on generic scripts and a scammer's ability to sound believable. Today, the same technology that powers helpful tools like AI phone calling is also being studied and used to fight back against these scams.