Most people are fairly good at reading, but not enough are good at reading between the lines. More often than not, there are certain things hidden in plain sight that may not catch your attention. The eyes of a system administrator are often glued to tasks like system maintenance and user administration. When engaged in many tasks at once, it is only human to overlook a few things like patch and antivirus updates, but it can cost an organization dearly in terms of data security.
As developers we all have our morning startup routine: make coffee, check slack/discord/email, read the latest news. One thing I do as part of my daily startup routine is check the Snyk vulnerability database for the latest open source vulnerabilities. It’s been especially interesting to see the types of exploits and vulnerabilities that appear in different ecosystems. For example, since May 2021 I’ve been watching the emergence of vulnerabilities in Tensorflow libraries.
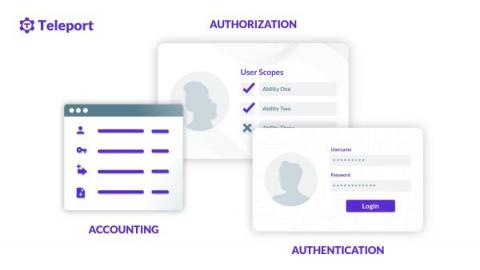
Authentication, authorization, and accounting, often called AAA or Triple-A, are sets of services and protocols that enable granular access control over computer networks. Before the popularity of mainstream HTTP-based authentication protocols such as OAuth and SAML, AAA protocols were the primary way to authenticate users or machines to network services.
As part of our ongoing efforts to offer you the most comprehensive and advanced SDLC protection capabilities, JFrog continues to boost the capabilities of our Xray security and compliance product. In this blog, we offer an overview of recent Xray improvements, all aimed at helping you fortify your software, reduce risk, scale security, streamline compliance and accelerate releases with confidence.
Today, we’re excited to announce a partnership with Sysdig to provide container and Kubernetes security together — from code to cluster. Together, Snyk and Sysdig can help developers secure code and containers in development, protect the runtime Kubernetes environment, and deliver feedback and visibility from production back to developers, eliminating the noise of container vulnerabilities.
Everybody’s talking about securing the DevOps pipeline and shifting security left.. AppSec tools like SAST (Static Application Security Testing), DAST (Dynamic Application Security Testing), and others that address issues in proprietary software have become staples of the developer’s security toolbox.
Today, we announced our entrance into the Static Application Security Testing (SAST) market. It’s a significant development for WhiteSource, which has until now been solely focused on open source software security. In this post, I explain why we decided to make this move beyond open source into proprietary code security, and the value it will bring to developers, security teams, and their organizations.
We’re excited to announce that our Snyk Business plan will now be available as a free trial. Many developers love Snyk products, but the true power of our platform is displayed when it’s used across an organization. No company wants to navigate a security incident, but ensuring that your entire SDLC is protected can be a challenge. The Snyk Business plan gives your organization access to empowering and easy-to-use tools to ensure nothing slips through the cracks.