Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Raising the Security Bar: Essential Measures to Combat Emerging Cyber Threats

Cyber threats are evolving all the time, and the pace of advancement is increasing. From malware and ransomware attacks to increasingly sophisticated phishing techniques and zero-day exploits, threat actors are constantly working to find new ways to breach our defenses, so we need to take proactive steps to raise security standards and keep our organizations on the front foot in the fight against cybercrime. In this piece, we'll discuss some essential measures you can take to do this, highlighting best practices and security technologies that can enable you to build a more threat-resilient organization.
Zero trust for public sector organizations

The “never trust, always verify” premise of Zero Trust requires a significant shift in how agencies evaluate security risks. Every transaction demands a risk assessment across every Zero Trust pillar — a tough task when the key data is locked in different systems and tools. But a unified data platform can essentially serve as the glue that connects all your systems, making them more integrated, accurate, and trustable.

Why SASE Makes Zero Trust Work

Gartner predicted that by early this year, over 60% of organizations would be using zero trust as their starting point for security. And no wonder. Cloud migration, hybrid work, and persistent threats have turned security into a minefield, exposing the cracks in old castle and moat, perimeter-based security architectures. Zero Trust aligns with how and where we work today, shifting the perimeter to individual users, devices, and applications—wherever they are.

Why East/West Traffic Needs Zero Trust

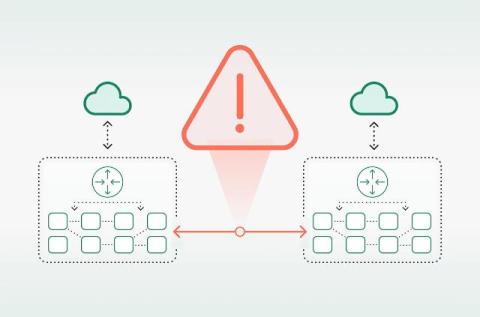
Zero trust is no longer just a concept—it’s essential. With cloud adoption, hybrid work, and increasingly sophisticated cyber threats, traditional perimeter security no longer suffices. Attackers exploit vulnerabilities inside networks, moving laterally undetected. Many organizations focus on securing north-south external-facing interactions while failing to monitor internal east-west traffic. This oversight exposes networks to ransomware, insider threats, and supply chain attacks.

Legacy NAC Can't Keep Up. UZTNA Is the Answer.

With the rise of hybrid work and IoT, the demand for secure, scalable, and adaptive network access has never been greater. Traditional network access control (NAC) was built for on-premises environments, focusing on visibility, device compliance, and access control. But it no longer meets modern security demands. This blog explores the limitations of traditional NAC and how Netskope offers a more dynamic and comprehensive solution for universal zero trust network access (UZTNA).

How Privileged Access Management Supports a Zero-Trust Strategy

Privileged Access Management (PAM) fits into a zero-trust strategy by strictly controlling access and monitoring privileged accounts, aligning with the zero-trust principle that users and devices should not be trusted by default. PAM ensures that privileged access is granted based on the principle of least privilege, continuous authentication and ongoing monitoring and auditing, reducing the risk of unauthorized access or privilege escalation.

Why Zero Trust Security Is Essential for Modern IT Infrastructure

In the modern IT landscape, cybercriminals are becoming more sophisticated and intentional about their attacks. Tools that help drive technological development are also being used as weapons against under-educated consumers. Between ransomware, phishing, and AI attacks, businesses must work harder than ever to protect their data effectively.