Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

MadeYouReset: An HTTP/2 vulnerability thwarted by Rapid Reset mitigations

On August 13, security researchers at Tel Aviv University disclosed a new HTTP/2 denial-of-service (DoS) vulnerability that they are calling MadeYouReset (CVE-2025-8671). This vulnerability exists in a limited number of unpatched HTTP/2 server implementations that do not sufficiently enforce restrictions on the number of times a client may send malformed frames. If you’re using Cloudflare for HTTP DDoS mitigation, you’re already protected from MadeYouReset.

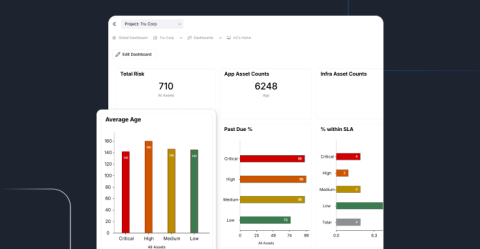
Enterprise-Grade Automation, Communication, and Risk: Nucleus Q2 Updates

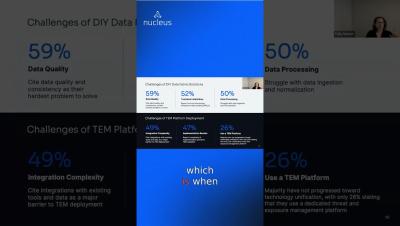
This release raises the bar for enterprise-grade vulnerability and exposure management. We’re delivering on the promise of smarter, faster risk reduction powered by automation, enriched data, and operational depth. From fix-level SLA tracking to scalable API workflows and stakeholder-ready reporting, every enhancement is designed to help teams do more with less, and prove it. Here’s a breakdown of some of the major product updates from Q2 2025.

Agentic Container Security with Snyk MCP Server

Did developers steal the spotlight of agentic workflows with the wave of AI coding assistants sweeping the media, startups, and tech? What about DevOps workflows, container security, and operating system vulnerability scanning? One of the most time consuming tasks of application security engineers and those responsible for production artifacts is tracking Common Vulnerabilities and Exposures (CVEs) and in what way they impact a bundled application.

Understanding Network Vulnerabilities and Mitigating Their Risks

Driving along on a dark highway late at night, you feel a jolt and hear a metallic crushing sound as your car hits an unknown object in the road. You nervously continue on your journey, until you see a bright light flashing on your dashboard. Your oil pressure is low because your car has been leaking oil since you hit that unknown object on the highway. Much like an unknown object in the road that leads to a slow leak, a network vulnerability can lead to a devastating data leakage or breach.

Seemplicity x SANS: The Future of Vulnerability Management is RemOps

Despite ongoing investment in detection tools, vulnerability management continues to underdeliver. Security teams don’t lack data. They lack the systems to act on it. According to our latest research, 91% of organizations report delays in remediation, and 41% say they struggle to make findings actionable. The result is a persistent backlog of exploitable vulnerabilities, compounded by manual workflows and poor coordination between teams.