Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How Often Should Organizations Perform DDoS Testing?

Most security teams have a firewall policy, a patch schedule, and a penetration testing calendar. DDoS resilience is often the exception, tested once, checked off, and forgotten until an actual attack exposes the gap. That's a real problem. Distributed denial-of-service threats aren't static, and neither is your infrastructure; the right answer to how often organizations should test depends on several variables, and the baseline is probably more frequent than you'd guess.
Featured Post

Why Data Governance Has Become a Critical Defence Against Ransomware in Healthcare

Ransomware and ransomware-style attacks can have a catastrophic impact within healthcare, where disruption directly impacts safety and continuity. Today's ransomware groups increasingly operate as sophisticated criminal enterprises, sharing tools, infrastructure, and expertise through ransomware-as-a-service (RaaS) models. This lowers the barrier to entry for cybercriminals while allowing experienced threat actors to focus their efforts on identifying and exploiting high-value targets.

Nobody Knows How Many AI Agent Breakouts There Have Been

Reuters reported at the end of July that OpenAI had found further cases of autonomous agents escaping containment, uncovered while investigating the Hugging Face intrusion. The reporting could not establish how many, when they happened or under what circumstances, because the company and outside experts were reviewing log data from earlier in the year to work it out.

AI Governance When the AI Is Inside the Network

Most AI governance guidance assumes the AI sits beside the business. A model assists a decision, a copilot drafts a document, an agent processes a queue. Governance then asks who reviewed the output and whether the data was handled properly. ‍ In a telecom network the AI is inside the product.

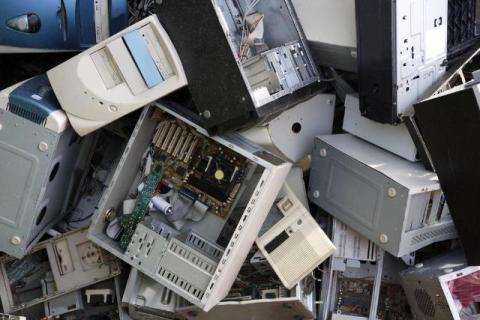
Electronics Recycling Laws and Regulations: What Georgia Businesses Should Know

A lot of Georgia business owners hear "there's no state e-waste law" and quietly assume that means old computers and servers can go straight into a regular dumpster. That assumption is wrong, and it's an expensive one to get wrong, since the absence of a state law doesn't mean the absence of any law at all.

Buying the Devices Is the Easy Part: The Complexity Behind Deploying Tech Across an Entire School District

Buying the tools is never the hard part. A district can approve a purchase order for interactive displays, robotics kits, or a cart of new devices in an afternoon. What's genuinely difficult, and what almost never gets talked about in the same conversation as the purchase, is everything that happens after the truck leaves: getting that equipment into forty classrooms, getting every teacher comfortable enough to actually use it, and making sure it's still being used well in April, not just during the excitement of week one.

Opera VPN Extensions What Users Should Check Before Installing One

The phrase "VPN" can describe different kinds of browser tools. Opera also has a built-in VPN feature, while third-party add-ons may route browser traffic through a proxy service. Before comparing features, establish exactly what traffic the extension handles and what it leaves untouched.