Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

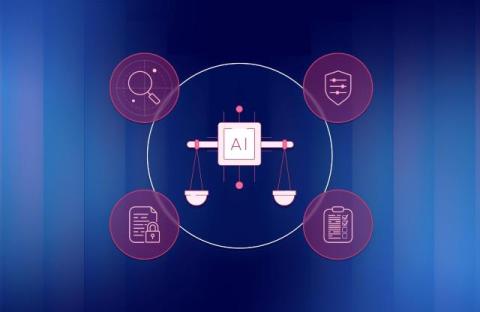
What Is AI Governance? A Practical Framework for Security Teams

The speed of AI integration is rapidly outpacing corporate governance capabilities. Generative AI is now embedded in development workflows and business applications, while agentic AI can make decisions and take actions with limited human intervention. That governance gap is becoming harder to ignore. Gartner predicts that more than 40% of agentic AI projects will be canceled by the end of 2027 because of escalating costs, unclear business value, or inadequate risk controls.
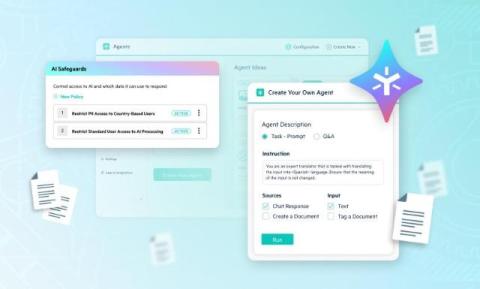
In AI Pilot Mode? Learn How to Scale AI Securely Without Shadow IT

You’ve seen the demos. You’ve run the pilots. Maybe you even deployed something that works, but is it scaling? Are your users utilizing it on a daily basis, or as intended? Or is it quietly gathering dust next to the last three tools that were supposed to change everything? Scaling AI the way most vendors describe it—connecting more tools and piping more data into more systems—doesn’t lead to progress or productivity. Rather, it results in additional risk.

CrowdStrike Expands Federal SOC Modernization Through CISA-Funded SIEMaaS

CISA has called SIEM-as-a-service (SIEMaaS) “the Rosetta Stone” for visibility for good reason. Federal defenders need to see what is happening across increasingly complex environments, understand what matters, and turn that context into action before an adversary achieves its objective.

Keeper Security Freshservice Workflow App Streamlines Vault and Privileged Access Request Process

Keeper Security, the leading zero-trust and zero-knowledge identity security and Privileged Access Management (PAM) platform, today announces a Freshservice Workflow integration that connects vault and privileged access requests to the ticketing systems IT and security teams already use. The integration lets agents fulfill Keeper vault access and approval requests – including Endpoint Privilege Manager and Cloud SSO device approvals – directly from a Freshservice ticket.

How Western Canada Lottery Corporation Is Modernizing 5,000 Retail Sites with Netskope SASE

Western Canada Lottery Corporation (WCLC) runs one of the world's most geographically dispersed retail networks: 5,000 lottery terminal locations across Manitoba, Saskatchewan, Alberta, and three northern territories. See how they replaced a fragmented multi-ISP setup with Netskope One SASE. In this 2-minute story, Adam Janssens, Director of Infrastructure and Operations, explains how WCLC: "The cost savings to move away from private connections to secure SD-WAN with Netskope is definitely multi-millions per year, which is a huge benefit to our organization and our provinces.".

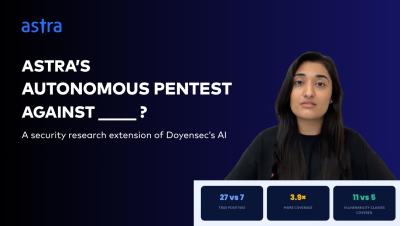
Astra's Autonomous Pentest Against Other Tool

Astra vs. Other Tool: Who Finds More Real Vulnerabilities? How does Astra Autonomous Pentesting compare with the other tool when it comes to finding real-world vulnerabilities? In this independent benchmark, Astra was tested against the other tool to evaluate vulnerability coverage, depth, and true-positive findings. The results: 27 true-positive vulnerabilities identified 3.9× more vulnerability coverage 11 distinct vulnerability classes discovered Deep testing across business logic and application behaviour.

How to Create a Hyper-V Virtual Switch | External, Internal & Private Switches

Hyper-V Virtual Switches are essential for connecting virtual machines to networks and managing communication between Hyper-V VMs, the host, and external networks. In this video, learn about the different types of Hyper-V Virtual Switches and when to use each one: External Virtual Switch – Connects VMs to the physical network Internal Virtual Switch – Enables communication between VMs and the Hyper-V host Private Virtual Switch – Enables communication between VMs on the same host.

Reconciling an AI Risk Estimate Against What Truly Happened

A model produces a figure, an event happens, and somebody asks whether the figure was right. It is the obvious question and it has almost no published answer, because the comparison is harder than it looks. ‍ A single realized loss cannot falsify a distribution. If a model puts a one percent chance on exceeding a threshold and the threshold is exceeded, the one percent case occurred, which is what the model said would sometimes happen. ‍