Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Certificate monitoring with TLS, chain, and post-quantum readiness

Most customers start CertKit with SSL host monitoring. On day one, you point CertKit at the systems you already run and get every certificate and when it expires. You start with confidence that you have everything under control. Then, you automate, letting CertKit take over the certificates as they need to be renewed. Each renewal is the last time you ever have to worry about that certificate.
How Aikido helps you meet SOC 2 Type 1 and Type 2

If you've ever gone through a SOC 2 audit, you know the drill. It’s weeks of screenshotting dashboards and chasing down evidence across some dozen tools, while hoping the auditor doesn't ask a follow-up question you can't answer. Fortunately, SOC 2 doesn't have to be that painful, especially if the tools you already use for security are generating the evidence for you as a byproduct of just doing their job. That's what Aikido Security can do for application and cloud security.

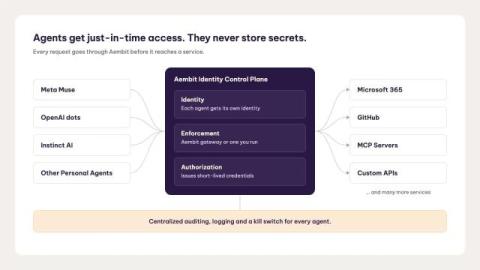
Five Ways AI Agents Actually Fail, and Why Most Security Programs Are Only Built for Two of Them

Most of the industry discourse on agentic AI risk has settled into a comfortable framing: agents get attacked the way models get attacked, through some form of prompt manipulation, and the fix is a better guardrail. I think that framing is dangerously incomplete, and I want to walk through five specific scenarios that make the case directly rather than abstractly. Two of them are manipulation. One exploits trust between agents rather than any single agent's behavior.

See Falcon for XIoT in Action.

CrowdStrike's Falcon for XIoT addresses challenges in managing complex industrial and clinical environments by providing visibility into operational assets. The solution helps teams prioritize vulnerabilities based on operational impact rather than severity alone, ensuring safe decisions while minimizing interruptions. Through a detailed investigation process, users can assess asset profiles, validate exposures, and implement controlled responses tailored to specific risks. This approach optimizes asset management and enhances safety in both operational technology (OT) and clinical settings.

Securing Your AI Agents: Native AI Detection and Response Across the Full Agentic Path

Enterprises are deploying AI agents at scale, and those agents are taking real business actions. Through LLMs, MCP servers, and APIs, they move money, access patient records, modify code, and send emails. The attack surface has fundamentally shifted, but most security programs are still focused on what an AI says rather than what it does.