Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Which Cloud Misconfigurations Would an Attacker Actually Exploit First?

A cloud security dashboard can produce hundreds of configuration issues in a single afternoon. There are a few small housekeeping concerns. Some leave customer files or administrative tools open for strangers to access. Security teams need to know what findings need quick attention, yet they have limited time to examine.
Staying Private and Safe on Random Chat Sites

Talking to a stranger online has a pull that social media lost long ago. There is no feed and no follower count, just a new person and an empty chat box. That openness is also the risk. When you know nothing about the person on the other side, ideally they know nothing about you either, and keeping it that way is most of what staying safe comes down to.

This Login Method is Stronger Than Your Password

Passkeys are a strong alternative to passwords. With a fingerprint scan, facial recognition or PIN, there’s nothing to remember so there’s nothing to steal. But most sites still require traditional passwords, so the smartest approach right now is to use both. Keeper Security stores your passwords and passkeys in the same vault, synced across all your devices.

One Feed, Many Clients: Running Multi-Tenant Threat Intelligence as an MSSP in 2027

his blog explains what multi-tenant threat intelligence is and why running one intelligence feed across many clients is one of the hardest jobs an MSSP has. It covers how a single compromise can spread across a client base, what MSSPs should look for in intelligence built for many tenants, and how the Cyber Security and Resilience Bill raises the stakes for UK providers.

Grandoreiro Malware: An Evolving Threat to Banking Customers

Grandoreiro is a malware family classified as a backdoor and spyware, first seen in April 2020, and is consistently described as a banking trojan focused on credential theft, remote fraud enablement, and control of compromised Windows systems. It has remained active through recurring campaigns, including a renewed wave in May and June 2026 that concentrated heavily on Latin America, especially Mexico, while also reaching parts of Europe and North America.

PHP2Shell and the end of the once-a-year pen test

On October 21, 2026, PHP shipped emergency fixes for two flaws that let anyone on the internet run code on a PHP web server, with no login. The weakness behind them had been flagged in 2024 and then sat, partly because nobody had proved it was exploitable. In 2026, researchers working with AI models proved it within days. Exploit attempts started before the fix shipped, and details leaked a day ahead of schedule. That sequence is the real story of PHP2Shell. The bug matters, but speed matters more.

Cybersecurity for Defence Networks: Protecting Critical Military Information and Systems

Digital technology plays an essential role in modern military operations. Defence organisations use interconnected systems to manage communications, exchange intelligence, coordinate personnel, and maintain operational readiness. However, increased connectivity also creates opportunities for cybercriminals and hostile actors to target sensitive information and critical infrastructure.

Cloudflare & Ping Identity: Identity Security in the Era of AI

As AI rapidly advances, identity security is undergoing a massive shift. Gavin Chen, Global Alliances at Cloudflare, shares how Cloudflare and Ping Identity are partnering to help organizations secure human users, non-human agents, and autonomous AI workflows—all while empowering businesses to innovate without friction.

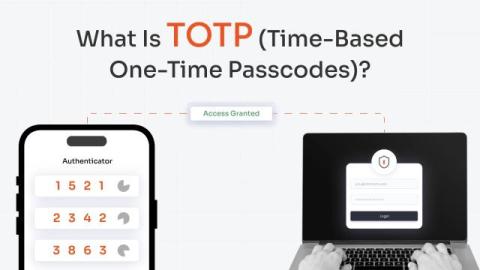
What Is TOTP? Security, Implementation, and Best Practices

TOTP (Time-Based One-Time Password) is an authentication algorithm that generates a unique, temporary numeric code using the current time as a moving factor. Typically, these codes are six digits long and automatically change every 30 seconds, providing a one-time verification code for authentication. TOTP uses a shared secret between the authentication service and the user's authenticator device, combining that secret with the current time to generate each code.