How to Reduce Overprivileged Kubernetes Service Accounts
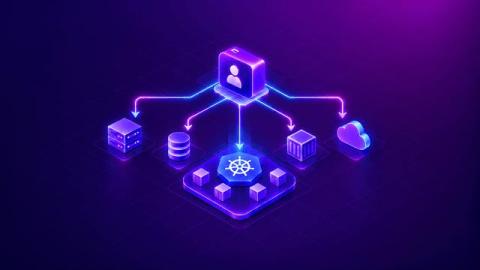
Overprivileged Kubernetes ServiceAccounts persist when broad RBAC, cloud IAM permissions, and long-lived credentials outlive their intended use. Reduce overprivileged access with least privileged RBAC, scoped cloud permissions, and short-lived certificates that eliminate static credentials. I spent two days last quarter tracking down why a developer could delete production secrets. The RBAC looked fine. The ClusterRoleBinding said edit, not cluster-admin.