This blog post is part thirty of the "Hunting with Splunk: The Basics" series. Shannon Davis provided the first half of this blog on pipe hunting in part twenty-nine, and will now run through the second half! – Ryan Kovar
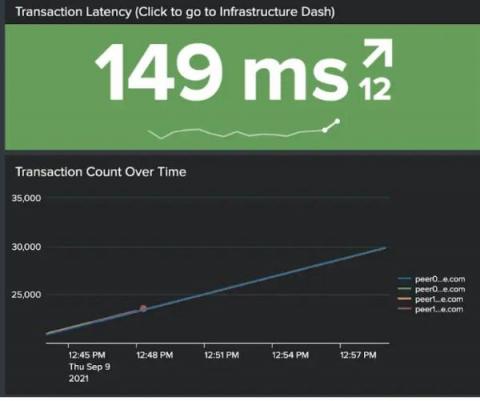
In this post, we demonstrate how to set up effective security monitoring of your Hyperledger Fabric infrastructure. We identify some common threats, recognize key data sources to monitor, and walk through using Splunk to ingest and visualize your data. This post follows Introducing Splunk App for Hyperledger Fabric and highlights the use of the app for security monitoring of blockchain infrastructure. We will address smart contract/chaincode security & monitoring in a follow-up post.
Even if an organization has developed a governance team, aligning integration decisions with business needs must be incorporated into the zero trust architecture. The company’s business model drives the applications chosen. The senior leadership team needs someone who can translate technology risks and apply them to business risks. For example, security might be an organization’s differentiator.
https://goteleport.com/docs/setup/guides/fluentd/
0:00 Intro
0:35 Forwarding events with Fluentd
6:54 Setting up ElasticSearch
11:02 Setting up FluentD
14:02 Viewing events in LogStash